Search result · source text not verified
Huntress
huntress.com ↗Get 24/7 SOC-backed EDR, ITDR, SIEM, & Security Awareness Training for enterprise-grade protection across all your environments. Threat actors use AI to generate sharper phishing lures and automate attacks, stripping much of the manual work out of cybercrime. Traditional SIEM deployments can generate mountains of data, leaving you to figure out what’s actually important while paying to store information you may never use.
Products
Huntress PlatformBuilt to deliver the next-level outcomes you need—Endpoint Integrity, Identity Resilience, Operational Readiness.
Athena EngineArtificial intelligence is changing cybersecurity on both sides. Explore how attackers are using AI and how Huntress puts it to work responsibly.
An AI-powered adversary is a cybercriminal or threat group that uses artificial intelligence to plan, build, or scale an attack, from writing custom malware and phishing lures to scanning environments for unpatched systems. AI sits on top of familiar tactics like credential theft and impersonation, making them faster, more personalized, and harder to detect than the manual versions security teams are used to. Source ↗
Threat actors use AI to generate sharper phishing lures and automate attacks, stripping much of the manual work out of cybercrime. As AI puts capable attacks in less-capable hands, defenders have to move faster without giving up their own judgment. Source ↗
Managed EDRGet full endpoint visibility, detection, and response.
Endpoint detection and response (EDR) is a technology that helps detect, investigate, and respond to threats that get past automated defenses like antivirus. It captures endpoint activity telemetry that is used to detect suspicious activity, support investigations with data and context, and enables a threat to be contained and remediated. Source ↗
Managed ITDRHuntress Managed ITDR protects Microsoft 365 identities around the clock. Stop credential theft, session hijacking, BEC and rogue apps with 24/7 AI-assisted SOC support.
Huntress Managed ITDR Shuts Down Identity Attacks
Source ↗With the majority of incidents now tied to identity threats, you need a purpose-built solution for continuous threat protection against critical risks like account takeovers and business email compromise (BEC). Session Hijacking Attackers grab session tokens—the digital keys that keep users logged in—and import them into their own browsers. No password is needed, just instant access. Our ITDR stops hackers from exploiting your systems and bypassing your 2FA/MFA. Learn More Credential Theft Identity is the new attack surface, and usernames and passwords are the new way into your business. Huntr
Managed SIEMHuntress Managed SIEM delivers enterprise-grade threat detection and compliance with 24/7 AI-assisted SOC, smart filtering, and predictable pricing — no chaos, no surprises.
Managed SATEmpower your teams with science-backed security awareness training.
We really enjoy that Huntress Managed SAT automates the learning and training assignments after you do the initial setup. We used to spend hours scheduling trainings/phishing campaigns manually with [our previous vendor]. Source ↗
Managed ISPMHuntress Managed Identity Security Posture Management (ISPM) closes the misconfigurations, gaps, and policy drift attackers rely on before they can be exploited. We define, deploy, and maintain gold-standard policies so your Secure Score goes up while your workload goes down.
Managed Identity Security Posture Management is a fully managed solution that hardens Microsoft 365 by finding and fixing misconfigurations, risky access, and policy drift. Huntress defines the gold standard, deploys the right controls, and keeps them enforced continuously so your posture keeps improving while your workload goes down. Source ↗
Huntress owns and maintains the identity security framework, so you don't have to create and define baselines. Managed ISPM continuously enforces best-practice policies across every organization you manage. We find and shut down the misconfigurations attackers love to exploit. Source ↗
Managed ESPMHuntress Managed ESPM is proactive endpoint protection made for all businesses, without the operational headaches. Nobody has time for unmanaged endpoint risk.
Proactive Endpoint Security Posture Management
Source ↗Explore how Huntress Managed ESPM makes it easy to proactively protect Windows endpoints and tougher for hackers to exploit them. App Control Hackers don’t just rely on their own tools—they also abuse legitimate trusted ones like RMMs and LOLBins . App Control dramatically shrinks an endpoint’s attack surface by giving you visibility over in-use apps and control of what’s allowed. Learn More Vulnerability Visibility Use insights from Microsoft Defender for Endpoint to get a centralized view of endpoint vulnerabilities and help prioritize remediation efforts. Learn More Unified Endpoint Visibil
API and IntegrationsWith the Huntress Agentic Security Platform, you can access your data where you need it most.
Pre-built integrations enable you to quickly connect your tech stack to automate work, streamline workflows, and minimize operational overhead. Huntress Managed SIEM connects with a growing list of log sources—giving you visibility across endpoints, networks, cloud environments, and more. Our integrations simplify ingestion and amplify detection, so you can focus on action, not configuration. Source ↗
ContactWant to chat with someone in sales, ask a question, or learn about one of our open roles?
_declassified Exposing hidden truths in the world of cybersecurity.Get a raw intel drop on the dark economy. Join Huntress and guest experts to unmask the business of modern cybercrime.
Threat LibraryThe Huntress Threat Library is your expert resource for in-depth insights on vulnerabilities, malware, ransomware, threat actors, and data breaches. Stay ahead with actionable threat intelligence.
Compare HuntressHuntress combines enterprise-grade protection with 24/7 human expertise. Don't choose between elite security and great support.
SearchOne managed platform across endpoint integrity, identity resilience, and operational readiness.
Start for FreeStart a fully functional Huntress trial: EDR, ITDR, ISPM, and SIEM free for 14 days, SAT for 21. Backed by a 24/7 human-led, AI-centric SOC.
No matching products or features.
Customer feedback
Search result · source text not verified
Huntress Email Security
Search result · source text not verified
Huntress alternatives
Search result · source text not verified
Zatanna, Huntress and Prime. FanArt by me
Search result · source text not verified
Adria Arjona is my ideal huntress fancast
Search result · source text not verified
Which design for Huntress do you prefer more and why?
Search result · source text not verified
Huntress - worth the money? : r/msp
Hi! This week, i did start the 21 day trial with Huntress. Luckily, it did not find anything… Now, i am having the same problem, as with every ...
Search result · source text not verified
What's going on with Huntress Culture, Employee ...
Huntress's culture has declined to the point that the direction of the company is in the balance. Employees no longer have any loyalty, because ...
Search result · source text not verified
Huntress Managed EDR Reviews & Product Details
Users consistently praise the 24/7 support and ease of deployment of Huntress Managed EDR, highlighting its ability to quickly detect and respond to threats, ...
Search result · source text not verified
Huntress Reviews 2026. Verified Reviews, Pros & Cons
Huntress is a quiet MDR. They are a trusted and reputable security company without the noise. Great value for the money! I like how it ...
Search result · source text not verified
Huntress User Reviews
"The platform is easy to use and offers strong malware protection, useful alerting, geo-blocking capabilities, and straightforward device management.
Search result · source text not verified
It feels like we're cyber's best kept secret. I'm... | Huntress ...
Read reviews of Huntress by verified sales professionals. Get insights on quota attainment, compensation, lead flow, and more on RepVue.
No feedback found.
Marketing & Ads
LinkedInHuntress
Original ad ↗
[Livestream] Follow the Money: How Your Stolen Data is Banking the Black Market
On October 27, Huntress' John Hammond sits down with Mastercard's Ann Johnson and investigative journalist Geoff White to follow the money from the moment it is taken to the ways defenders hit back. Save your spot for the season finale of _declassified now.
Learn more
First shown Oct 19, 2026 · Last shown Oct 28, 2026Landing page
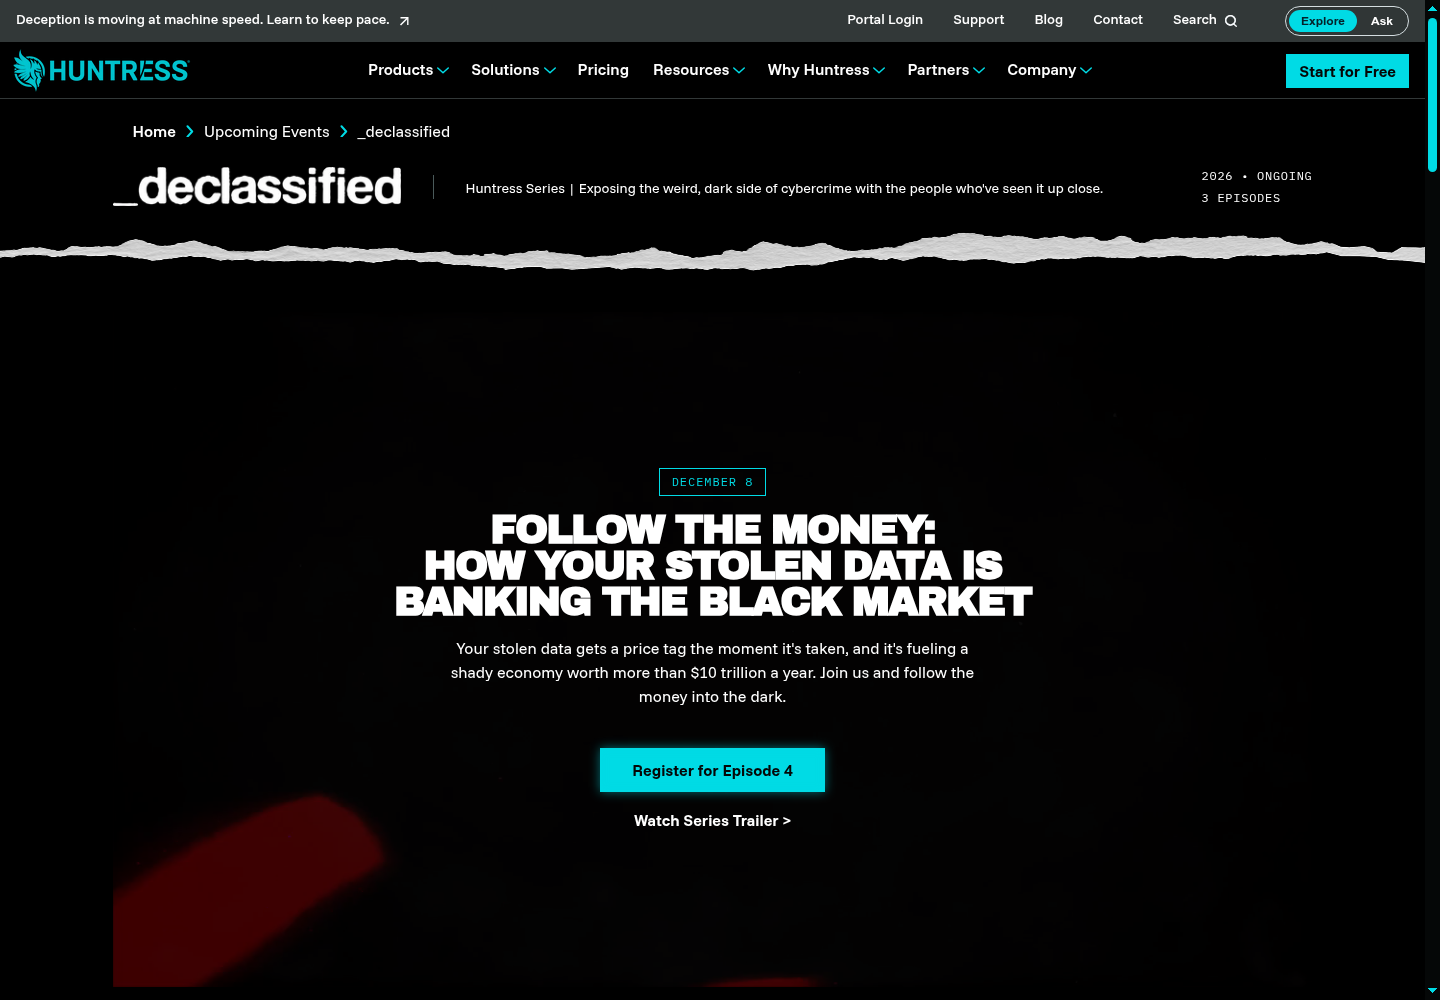 Captured Nov 10, 2026_declassified: Real-World Cybercrime & Security Insights | Huntress ↗
GoogleHuntress Labs Inc.
Original ad ↗Full-Stack MSP Protection - Multi-Tenant Ready EDR
Built for MSPs: multi-tenant, fast to deploy, and priced to protect your margins. Clients expect protection that...
First shown Sep 27, 2026 · Last shown Nov 10, 2026Landing page unavailable: the ad source did not supply a destination URL.
LinkedInHuntress
Original ad ↗Hey %FIRSTNAME%, I’m Harliegh from Huntress. You already know if your security vendor is costing you time, margin, or client confidence—the issue is the contract. The Huntress Buyout Program takes that off the table. If you qualify, we cover the cost of Huntress for the rest of your current contract with another vendor, so switching now doesn’t mean paying twice going into 2027. You get managed detection and response backed by a 24/7 SOC, plus a migration plan built to move your clients with minimal disruption. Book a quick buyout review, and we’ll walk through your setup, your remaining term, and whether you qualify. And as a thank you for your time, we’ll send you a $20 gift card for coffee and a sweet treat after the review!
Let’s talk
First shown Oct 26, 2026 · Last shown Nov 10, 2026Landing page unavailable: the ad source did not supply a destination URL.
LinkedInHuntress
Original ad ↗[Livestream] Follow the Money: How Your Stolen Data is Banking the Black Market
Your stolen data gets a price tag the moment it’s taken. Follow the money with Huntress' John Hammond, Mastercard’s Ann Johnson, and investigative journalist Geoff White on the season finale of _declassified, live on Oct 27.
Learn more
Landing page unavailable: the ad source did not supply a destination URL.
GoogleHuntress Labs Inc.
Original ad ↗Deploys in Minutes, Not Months
One affordable price per endpoint. No add-ons, no extra tiers, no multi-year contracts.
Learn more
First shown Sep 21, 2026 · Last shown Nov 10, 2026
GoogleHuntress Labs Inc.
Original ad ↗Deploys in Minutes, Not Months
Deployable across your network in minutes. See how Huntress compares.
Learn more
First shown Sep 21, 2026 · Last shown Nov 10, 2026GoogleHuntress Labs Inc.
Original ad ↗Deploys in Minutes, Not Months
One affordable price per endpoint. No add-ons, no extra tiers, no multi-year contracts.
Learn more
First shown Sep 21, 2026 · Last shown Nov 10, 2026LinkedInHuntress
Original ad ↗[Livestream] Follow the Money: How Your Stolen Data is Banking the Black Market
On 8 December, Huntress' John Hammond sits down with Mastercard's Ann Johnson and investigative journalist Geoff White to follow the money from the moment it is taken to the ways defenders hit back. Save your spot for the season finale of _declassified now.
Learn more
Landing page unavailable: the ad source did not supply a destination URL.
GoogleHuntress Labs Inc.
Original ad ↗
Identity Is the New Attack Surface
Identity and configuration are your real attack surface. Try it free
Video ↗First shown Sep 21, 2026 · Last shown Nov 10, 2026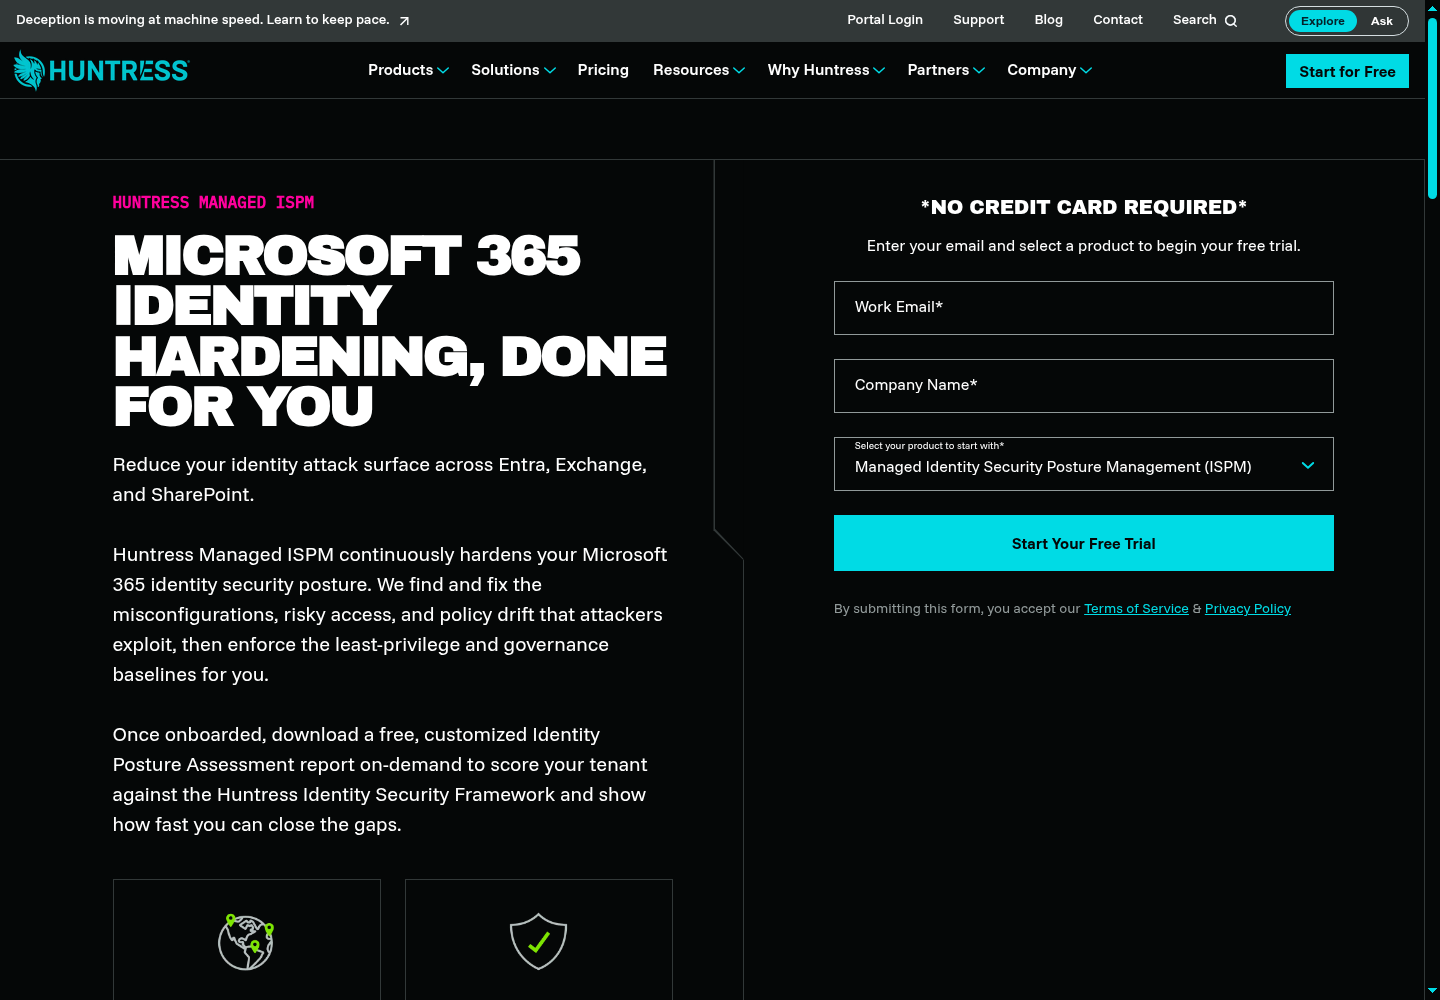
GoogleHuntress Labs Inc.
Original ad ↗View original ad ↗
First shown Sep 21, 2026 · Last shown Nov 10, 2026Landing page unavailable: the ad source did not supply a destination URL.
GoogleHuntress Labs Inc.
Original ad ↗Harden M365 Before the Incident
Identity and configuration are your real attack surface. Try it free
Video ↗First shown Sep 21, 2026 · Last shown Nov 10, 2026GoogleHuntress Labs Inc.
Original ad ↗ First shown Sep 4, 2026 · Last shown Nov 10, 2026
Landing page unavailable: the ad source did not supply a destination URL.
LinkedInHuntress
Original ad ↗Hey %FIRSTNAME%, I’m Harliegh from Huntress. You already know if your security vendor is costing you time, margin, or client confidence—the issue is the contract. The Huntress Buyout Program takes that off the table. If you qualify, we cover the cost of Huntress for the rest of your current contract with another vendor, so switching now doesn’t mean paying twice going into 2027. You get managed detection and response backed by a 24/7 SOC, plus a migration plan built to move your clients with minimal disruption. Book a quick buyout review, and we’ll walk through your setup, your remaining term, and whether you qualify. And as a thank you for your time, we’ll send you a $20 gift card for coffee and a sweet treat after the review!
Let’s talk
First shown Oct 26, 2026 · Last shown Nov 10, 2026Landing page unavailable: the ad source did not supply a destination URL.
LinkedInHuntress
Original ad ↗
[Livestream] Follow the Money: How Your Stolen Data is Banking the Black Market
Your stolen data gets a price tag the moment it’s taken. On October 27, follow the money with Huntress' John Hammond, Mastercard’s Ann Johnson, and investigative journalist Geoff White on the season finale of _declassified. Save your spot today.
Learn more
Landing page unavailable: the ad source did not supply a destination URL.
GoogleHuntress Labs Inc.
Original ad ↗ First shown May 14, 2025 · Last shown Nov 10, 2026
Landing page unavailable: the ad source did not supply a destination URL.
LinkedInHuntress
Original ad ↗Hey %FIRSTNAME%, I’m Harliegh from Huntress. You already know if your security vendor is costing you time, margin, or client confidence—the issue is the contract. The Huntress Buyout Program takes that off the table. If you qualify, we cover the cost of Huntress for the rest of your current contract with another vendor, so switching now doesn’t mean paying twice going into 2027. You get managed detection and response backed by a 24/7 SOC, plus a migration plan built to move your clients with minimal disruption. Book a quick buyout review, and we’ll walk through your setup, your remaining term, and whether you qualify. And as a thank you for your time, we’ll send you a $20 gift card for coffee and a sweet treat after the review!
Book a buyout review
Landing page unavailable: the ad source did not supply a destination URL.
LinkedInHuntress
Original ad ↗[Livestream] Follow the Money: How Your Stolen Data is Banking the Black Market
Your stolen data gets a price tag the moment it’s taken. Follow the money with Huntress' John Hammond, Mastercard’s Ann Johnson, and investigative journalist Geoff White on the season finale of _declassified, live on 8 Dec.
Learn more
Landing page unavailable: the ad source did not supply a destination URL.
GoogleHuntress Labs Inc.
Original ad ↗This isn’t the security awareness training you’re used to
Video ↗First shown Jun 30, 2026 · Last shown Nov 10, 2026Landing page unavailable: the ad source did not supply a destination URL.
GoogleHuntress Labs Inc.
Original ad ↗This isn’t the security awareness training you’re used to
Video ↗First shown Jun 30, 2026 · Last shown Nov 10, 2026Landing page unavailable: the ad source did not supply a destination URL.
GoogleHuntress Labs Inc.
Original ad ↗Give clients SAT that lowers human risk, not just checks a box. Book a demo today.
Video ↗First shown Jun 30, 2026 · Last shown Nov 10, 2026Landing page unavailable: the ad source did not supply a destination URL.
GoogleHuntress Labs Inc.
Original ad ↗ First shown Jul 1, 2026 · Last shown Nov 10, 2026
Landing page unavailable: the ad source did not supply a destination URL.
GoogleHuntress Labs Inc.
Original ad ↗View original ad ↗
First shown Jul 21, 2026 · Last shown Nov 10, 2026Landing page unavailable: the ad source did not supply a destination URL.
GoogleHuntress Labs Inc.
Original ad ↗View original ad ↗
First shown Jul 21, 2026 · Last shown Nov 10, 2026Landing page unavailable: the ad source did not supply a destination URL.
GoogleHuntress Labs Inc.
Original ad ↗View original ad ↗
First shown Jul 21, 2026 · Last shown Nov 10, 2026Landing page unavailable: the ad source did not supply a destination URL.
New pages
brute force sentry ↗
declassified money train episode four ↗
attackers turn mdm into remote access ↗
camera management software compromise malware ↗
connectwise attack ai ↗
amazon clickfix finger ↗
huntress crn annual report card 2026 ↗
human risk management ↗
identity security ↗
algapsa huntress api integration ↗
clickfix bec tragic quadrant doris ↗
cmmc level 2 non negotiable requirements ↗
rapid response and vulnerabilities ↗
inside huntress ↗
ai ↗
ahsaycbs flaws exploit ↗
agentic soc ↗
chatgpt custom gpts clickfix rat ↗
culture at speed ↗
darkme rat abandons exploits ↗
claude fable api recall ↗
ai attackers machine speed huntress athena ↗
ad rms slc encryption key ↗
See How AI Search Works ↗
huntress inc 5000 2026 ↗
ai attack surface ↗
cmmc phase 2 pause and far council rule ↗
ad rms architecture and recon ↗
cyberattack readiness ↗
declassified cybercrime episode three ↗
australian signals directorate cyber priorities ↗
leverage AI Centric workflows ↗
audit readiness gap ↗
AI is central to how the SOC operates ↗
huntress inc best workplaces 2026 ↗
black hat def con standouts ↗
cybersecurity budget ↗
akira hits safe mode ransomware rebooting around edr ↗
bank spam rmm ↗
business reflection 250m arr ↗
custom html for custom phishing ↗
Read more about Meet Athena, Our Agentic SOC Analyst ↗
citrixbleed 2 dragonforce ransomware ↗
ai arms race in recruiting ↗
infrastructure, and a separate ROPC credential-replay attack from LSHIY LLC ↗
ai coded malware vibe coding active directory ↗
cybersecurity lessons taylor swift wedding ↗
canada localized managed phishing ↗
cloud application security ↗
advanced phishing tradecraft ↗
akira ransomware limewire data exfiltration ↗
First archived Source ↗
all blog posts ↗
deceptive installers macos infostealers ↗
declassified cybercrime episode two ↗
cmmc msp readiness check ↗
cloud security challenges ↗
huntress itdr crn annual report card ↗
huntress sans cybersecurity company of the year awards ↗
First archived Source ↗
identity protection ↗
cybersecurity frameworks ↗
adversary tactics team ↗
clickfix castleloader backgroundfix ↗
huntress named best managed detection and response security service ↗
sc awards best siem solution huntress ↗
ai powered attack workflows ↗
codex part two ↗
axios npm compromise ↗
First archived Source ↗
rapid responses ↗
codex part one ↗
security posture management ↗
huntress named security awareness training platform of the year ↗
First archived Source ↗
security awareness training ↗
building resilient security teams ↗
First archived Source ↗
healthcare security ↗
siem and security operations ↗
First archived Source ↗
endpoint detection and response ↗
First archived Source ↗
ai and the modern soc ↗
threat research ↗
First archived Source ↗
attacker tradecraft ↗
First archived Source ↗
msp playbook ↗
First archived Source ↗
security fundamentals ↗
First archived Source ↗
from the front lines ↗
deepfake three finger test ↗
declassified cybercrime episode one ↗
3 2 1 backup rule ↗
data exfiltration threat actor infrastructure exposed ↗
daisy chaining rogue rmm tools ↗
app domain manager injection ↗
ai enhanced candidate fraud ↗
clickfix matanbuchus astarionrat analysis ↗
active exploitation solarwinds web help desk cve 2025 26399 ↗
ai 2025 faster attacks same tradecraft ↗
cmmc opportunity cost msp challenges ↗
active exploitation gladinet centrestack triofox insecure cryptography vulnerability ↗
datacenter infrastructure and identity attacks ↗
amos stealer chatgpt grok ai trust ↗
clickfix malware buried in images ↗
Modified Source ↗
hidden competition ↗
Modified Source ↗
cve 2023 50387 ↗
Modified Source ↗
cve 2024 1708 ↗
Modified Source ↗
One Bad Click Could Cost You Everything: Huntress Phishing Prevention Keeps You Secure ↗
Modified Source ↗
huntress best managed security service sc awards europe 2026 ↗
Modified Source ↗
huntress fortune cyber 60 2026 ↗
Modified Source ↗
huntress inc power partner 2026 ↗
Modified Source ↗
huntress mes midmarket 100 2026 ↗
Modified Source ↗
huntress soc team of the year cybersecurity stars 2026 ↗
Modified Source ↗
blackhat2026 ↗
The Huntress Cybersecurity Blog ↗
Modified Source ↗
ahsaycbs webshells ↗
Modified Source ↗
employee spotlight sasha roshan ↗
Modified Source ↗
n able disables cloud services following disclosure of able2shell exploit chains ↗
Modified Source ↗
awards and accolades ↗
Modified Source ↗
leadership ↗
Modified Source ↗
our story ↗
Modified Source ↗
press ↗
Modified Source ↗
series c ↗
Modified Source ↗
the journey to two million endpoints ↗
Modified Source ↗
Contact Us ↗
Modified Source ↗
cookie policy ↗
Modified Source ↗
guide to algorithms ↗
Modified Source ↗
incident responder ↗
Modified Source ↗
principle of least privilege cybersecurity guide ↗
Modified Source ↗
3g in cybersecurity ↗
Modified Source ↗
adversarial ai cybersecurity threats defenses ↗
Modified Source ↗
adversary in the middle attack ↗
Modified Source ↗
adware protection ↗
Modified Source ↗
agent vs agentless security ↗
Modified Source ↗
agentic ai security ↗
Modified Source ↗
agentic threat actor ↗
Modified Source ↗
ai security specialist ↗
Modified Source ↗
air gap security ↗
Modified Source ↗
anonymizer ↗
Modified Source ↗
anti fraud systems ↗
Modified Source ↗
anti spyware ↗
Modified Source ↗
application access ↗
Modified Source ↗
application delivery controller ↗
Modified Source ↗
application exploits and vulnerabilities ↗
Modified Source ↗
application security engineer ↗
Modified Source ↗
application security posture management ↗
Modified Source ↗
application services ↗
Modified Source ↗
arp spoofing ↗
Modified Source ↗
artificial intelligence in cybersecurity ↗
Modified Source ↗
asoc ↗
Modified Source ↗
asset in cybersecurity ↗
Modified Source ↗
audit events ↗
Modified Source ↗
automated threat intelligence ↗
Modified Source ↗
autoscanning ↗
Modified Source ↗
aws cloud security ↗
Modified Source ↗
blackholing ↗
Modified Source ↗
blockchain security expert ↗
Modified Source ↗
bootkit prevention guide ↗
Modified Source ↗
bot activity ↗
Modified Source ↗
bot mitigation ↗
Modified Source ↗
bracketing ↗
Modified Source ↗
bring your own device byod ↗
Modified Source ↗
browser extensions ↗
Modified Source ↗
browser in the browser attack ↗
Modified Source ↗
bug bounty hunter ↗
Modified Source ↗
built in tools ↗
Modified Source ↗
business compliance regulations ↗
Modified Source ↗
c2 command and control ↗
Modified Source ↗
centralized logging ↗
Modified Source ↗
clientless vpn ↗
Modified Source ↗
cloud compliance solutions ↗
Modified Source ↗
cloud governance ↗
Modified Source ↗
cloud networking ↗
Modified Source ↗
cloud security frameworks ↗
Modified Source ↗
cloud security posture management ↗
Modified Source ↗
code security ↗
Modified Source ↗
compiler security ↗
Modified Source ↗
compliance analyst role explained ↗
Modified Source ↗
configuration management tools ↗
Modified Source ↗
consent fix ↗
Modified Source ↗
cross site request forgery ↗
Modified Source ↗
cryptojacking ↗
Modified Source ↗
cyber operations ↗
Modified Source ↗
cybersecurity analytics ↗
Modified Source ↗
cybersecurity manager ↗
Modified Source ↗
cybersecurity monitoring services ↗
Modified Source ↗
cybersecurity transformation ↗
Modified Source ↗
dark web activity ↗
Modified Source ↗
data aggregation ↗
Modified Source ↗
data encryption ↗
Modified Source ↗
data exfiltration ↗
Modified Source ↗
data flow mapping ↗
Modified Source ↗
data loss prevention ↗
Modified Source ↗
data onboarding ↗
Modified Source ↗
data plane ↗
Modified Source ↗
data portability ↗
Modified Source ↗
data privacy ↗
Modified Source ↗
data protection vs data security ↗
Modified Source ↗
data sovereignty ↗
Modified Source ↗
data traffic ↗
Modified Source ↗
deep web vs dark web cybersecurity guide ↗
Modified Source ↗
device code phishing ↗
Modified Source ↗
digital footprint ↗
Modified Source ↗
disaster recovery plan ↗
Modified Source ↗
disinformation campaign ↗
Modified Source ↗
dll hijacking ↗
Modified Source ↗
dmz ↗
Modified Source ↗
dns filtering ↗
Modified Source ↗
dns protection ↗
Modified Source ↗
dns sinkholing ↗
Modified Source ↗
doc file extension ↗
Modified Source ↗
domain admin groups ↗
Modified Source ↗
domain spoofing ↗
Modified Source ↗
drive by download attack ↗
Modified Source ↗
dump data ↗
Modified Source ↗
dwell time in cybersecurity ↗
Modified Source ↗
dynamic acls ↗
Modified Source ↗
edr evasion ↗
Modified Source ↗
elevation control endpoint management ↗
Modified Source ↗
email spoofing ↗
Modified Source ↗
event logging ↗
Modified Source ↗
exploit developer ↗
Modified Source ↗
exploit kit ↗
Modified Source ↗
exploit pack ↗
Modified Source ↗
exploitation in the wild itw ↗
Modified Source ↗
extended detection and response xdr ↗
Modified Source ↗
extensible authentication protocol ↗
Modified Source ↗
false positive viruses ↗
Modified Source ↗
fileless malware ↗
Modified Source ↗
firewall costs ↗
Modified Source ↗
fisma ↗
Modified Source ↗
fisma vs nist ↗
Modified Source ↗
form grabber ↗
Modified Source ↗
fqdn cybersecurity networking ↗
Modified Source ↗
fraud prevention ↗
Modified Source ↗
fraudulent wire transfers ↗
Modified Source ↗
ftc safeguards rule ↗
Modified Source ↗
full disk encryption guide ↗
Modified Source ↗
gdpr cybersecurity ↗
Modified Source ↗
generic device ↗
Modified Source ↗
geofencing ↗
Modified Source ↗
google dorking ↗
Modified Source ↗
grabber ↗
Modified Source ↗
guide to firewalls ↗
Modified Source ↗
hackers defined ↗
Modified Source ↗
handshake protcol ↗
Modified Source ↗
hoax attacks ↗
Modified Source ↗
homograph attacks explained ↗
Modified Source ↗
how to prevent information theft ↗
Modified Source ↗
http3 ↗
Modified Source ↗
human identity ↗
Modified Source ↗
human risk management ↗
Modified Source ↗
identity abuse ↗
Modified Source ↗
identity access management specialist role ↗
Modified Source ↗
identity lifecycle management ↗
Modified Source ↗
identity theft prevention for business ↗
Modified Source ↗
ieee 802 1 ↗
Modified Source ↗
information security ↗
Modified Source ↗
infrastructure as a service ↗
Modified Source ↗
ingress controller ↗
Modified Source ↗
injection attack ↗
Modified Source ↗
interactive login ↗
Modified Source ↗
ioc vs ioa ↗
Modified Source ↗
iot security engineer ↗
Modified Source ↗
ip address ↗
Modified Source ↗
laas logging as a service ↗
Modified Source ↗
living off the land attack examples ↗
Modified Source ↗
living off the land attacks ↗
Modified Source ↗
local area network lan ↗
Modified Source ↗
log management ↗
Modified Source ↗
log retention ↗
Modified Source ↗
log rotation ↗
Modified Source ↗
log streaming ↗
Modified Source ↗
low code platform security ↗
Modified Source ↗
machine learning ↗
Modified Source ↗
malvertising ↗
Modified Source ↗
malware analyst explained ↗
Modified Source ↗
malware packer ↗
Modified Source ↗
managed detection response explained ↗
Modified Source ↗
managed it services ↗
Modified Source ↗
mean time to respond ↗
Modified Source ↗
mfa tokens ↗
Modified Source ↗
mobile device management ↗
Modified Source ↗
mobile threat defense ↗
Modified Source ↗
monitoring vs observability ↗
Modified Source ↗
mtan ↗
Modified Source ↗
multihoming ↗
Modified Source ↗
nat rules ↗
Modified Source ↗
near field communication ↗
Modified Source ↗
network control ↗
Modified Source ↗
network detection response ↗
Modified Source ↗
network security engineer role ↗
Modified Source ↗
next generation antivirus ngav ↗
Modified Source ↗
nginx ↗
Modified Source ↗
nist role in cybersecurity frameworks guide ↗
Modified Source ↗
offensive security ↗
Modified Source ↗
over the air technology ↗
Modified Source ↗
owasp security top 10 cybersecurity guide ↗
Modified Source ↗
pass the cookie ↗
Modified Source ↗
pass the hash ↗
Modified Source ↗
password management ↗
Modified Source ↗
password security storage ↗
Modified Source ↗
password spraying ↗
Modified Source ↗
passwordless security ↗
Modified Source ↗
payload in cybersecurity ↗
Modified Source ↗
pci dss cybersecurity ↗
Modified Source ↗
physical security tester ↗
Modified Source ↗
pig butchering scam ↗
Modified Source ↗
platform as a service paas ↗
Modified Source ↗
platform consolidation ↗
Modified Source ↗
positive digital footprint ↗
Modified Source ↗
post office protocol ↗
Modified Source ↗
ppc security ↗
Modified Source ↗
privileged access management ↗
Modified Source ↗
prompt injection attack ↗
Modified Source ↗
quantum computing defined ↗
Modified Source ↗
rainbow table defined ↗
Modified Source ↗
ram scraper ↗
Modified Source ↗
ransomware as a service ↗
Modified Source ↗
ransomware recovery guide ↗
Modified Source ↗
rc5 algorithm ↗
Modified Source ↗
recovery time objective ↗
Modified Source ↗
remote access trojan ↗
Modified Source ↗
remote desktop protocol ↗
Modified Source ↗
remote monitoring management tools ↗
Modified Source ↗
remote shell ↗
Modified Source ↗
repacking ↗
Modified Source ↗
request for comments ↗
Modified Source ↗
risk compliance specialst role ↗
Modified Source ↗
rogue access point ↗
Modified Source ↗
rogue apps 101 ↗
Modified Source ↗
role based access control ↗
Modified Source ↗
role of cybersecurity researchers ↗
Modified Source ↗
role of security engineer ↗
Modified Source ↗
romance scams ↗
Modified Source ↗
root access ↗
Modified Source ↗
saas security posture management ↗
Modified Source ↗
sandbox escape ↗
Modified Source ↗
sdk it ↗
Modified Source ↗
sec cybersecurity disclosure rules ↗
Modified Source ↗
secops ↗
Modified Source ↗
secure element application ↗
Modified Source ↗
security director ↗
Modified Source ↗
security issues ↗
Modified Source ↗
security observability ↗
Modified Source ↗
security operations reports ↗
Modified Source ↗
security orchestration ↗
Modified Source ↗
security proof of concept ↗
Modified Source ↗
semi structured data ↗
Modified Source ↗
seo poisoning ↗
Modified Source ↗
server monitoring ↗
Modified Source ↗
Learn More ↗
Modified Source ↗
shadow ai ↗
Modified Source ↗
sid security identifier ↗
Modified Source ↗
single factor authentication ↗
Modified Source ↗
sip proxy ↗
Modified Source ↗
snmp networking ↗
Modified Source ↗
snort rules ↗
Modified Source ↗
software as a service ↗
Modified Source ↗
software security ↗
Modified Source ↗
spf dkim dmarc explained ↗
Modified Source ↗
spider in computer ↗
Modified Source ↗
spyware ↗
Modified Source ↗
sql injection ↗
Modified Source ↗
ssl offloading ↗
Modified Source ↗
ssl termination ↗
Modified Source ↗
ssl traffic ↗
Modified Source ↗
stack trace explained ↗
Modified Source ↗
stateful firewall ↗
Modified Source ↗
stateful vs stateless firewall ↗
Modified Source ↗
static application security testing ↗
Modified Source ↗
stealthware ↗
Modified Source ↗
structured logging ↗
Modified Source ↗
syslog explained ↗
Modified Source ↗
system development ↗
Modified Source ↗
system security plan ↗
Modified Source ↗
tabletop excercise ↗
Modified Source ↗
the chief information security officers guide to cybersecurity leadership ↗
Modified Source ↗
threat actor profiling ↗
Modified Source ↗
threat actors defined ↗
Modified Source ↗
threat intelligence analysts ↗
Modified Source ↗
threat intelligence feed ↗
Modified Source ↗
threat intelligence platform ↗
Modified Source ↗
threat landscape defined ↗
Modified Source ↗
time to ransom ↗
Modified Source ↗
token ↗
Modified Source ↗
token theft ↗
Modified Source ↗
tor mirrors ↗
Modified Source ↗
trojan horse ↗
Modified Source ↗
trusted platform module tpm cybersecurity guide ↗
Modified Source ↗
ttps ↗
Modified Source ↗
type confusion ↗
Modified Source ↗
unauthorized access ↗
Modified Source ↗
unified audit explained ↗
Modified Source ↗
url spoofing ↗
Modified Source ↗
user identity management ↗
Modified Source ↗
ussd ↗
Modified Source ↗
vast threat modeling ↗
Modified Source ↗
vulnerability management lifecycle ↗
Modified Source ↗
web application firewall waf ↗
Modified Source ↗
website application security ↗
Modified Source ↗
what are backdoor attacks ↗
Modified Source ↗
what are buffer overflow attacks ↗
Modified Source ↗
what are cis benchmarks ↗
Modified Source ↗
what are cloud security best practices ↗
Modified Source ↗
what are common cash app scams ↗
Modified Source ↗
what are cookies ↗
Modified Source ↗
what are crud operations ↗
Modified Source ↗
what are executables ↗
Modified Source ↗
what are iis logs ↗
Modified Source ↗
what are integrations ↗
Modified Source ↗
what are log files ↗
Modified Source ↗
what are nist 800 171a assessment objective ↗
Modified Source ↗
what are outbound phishing attacks ↗
Modified Source ↗
what are remote administration tools rats ↗
Modified Source ↗
what are security dependencies ↗
Modified Source ↗
what are virtual machines ↗
Modified Source ↗
what are voip networks ↗
Modified Source ↗
what are yara rules ↗
Modified Source ↗
what are zero day vulnerabilities ↗
Modified Source ↗
what does a cyber risk analyst do ↗
Modified Source ↗
what does a forensic analyst do cybersecurity ↗
Modified Source ↗
what does a reverse engineer do cybersecurity ↗
Modified Source ↗
what does security analyst do ↗
Modified Source ↗
what does zero trust architecture do ↗
Modified Source ↗
what is 419 scam ↗
Modified Source ↗
what is a bat file ↗
Modified Source ↗
what is a blue team ↗
Modified Source ↗
what is a browser helper objective ↗
Modified Source ↗
what is a brute force attack ↗
Modified Source ↗
what is a callback scam ↗
Modified Source ↗
what is a com file ↗
Modified Source ↗
what is a computer virus ↗
Modified Source ↗
what is a cryptographer ↗
Modified Source ↗
what is a decompiler cybersecurity reverse engineering guide ↗
Modified Source ↗
what is a deepfake ↗
Modified Source ↗
what is a dll side loading ↗
Modified Source ↗
what is a dns changer ↗
Modified Source ↗
what is a downloader ↗
Modified Source ↗
what is a foothold ↗
Modified Source ↗
what is a log format ↗
Modified Source ↗
what is a parser ↗
Modified Source ↗
what is a purple team cybersecurity ↗
Modified Source ↗
what is a red team ↗
Modified Source ↗
what is a rootkit ↗
Modified Source ↗
what is a scam ↗
Modified Source ↗
what is a script kiddie ↗
Modified Source ↗
what is a session ↗
Modified Source ↗
what is a text bomb ↗
Modified Source ↗
what is a user agent ↗
Modified Source ↗
what is a vulnerability ↗
Modified Source ↗
what is a web server ↗
Modified Source ↗
what is access logging ↗
Modified Source ↗
what is active directory ↗
Modified Source ↗
what is active directory auditing ↗
Modified Source ↗
what is active discovery ↗
Modified Source ↗
what is address space layout randomization aslr ↗
Modified Source ↗
what is adfs ↗
Modified Source ↗
what is advanced encryption standard ↗
Modified Source ↗
what is adware ↗
Modified Source ↗
what is air gapping ↗
Modified Source ↗
what is allowlisting ↗
Modified Source ↗
what is an app server cybersecurity ↗
Modified Source ↗
what is an application firewall ↗
Modified Source ↗
what is an attack vector ↗
Modified Source ↗
what is an audit log ↗
Modified Source ↗
what is an endpoint cybersecurity ↗
Modified Source ↗
what is an exploit ↗
Modified Source ↗
what is anonfiles ↗
Modified Source ↗
what is antivirus affiliate program ↗
Modified Source ↗
what is api gateway ↗
Modified Source ↗
what is api security ↗
Modified Source ↗
what is application performance monitoring ↗
Modified Source ↗
what is application security ↗
Modified Source ↗
what is application whitelisting ↗
Modified Source ↗
what is apt group ↗
Modified Source ↗
what is arp spoofing ↗
Modified Source ↗
what is asymmetric algorithm ↗
Modified Source ↗
what is audit file ↗
Modified Source ↗
what is authentication ↗
Modified Source ↗
what is big game hunting ↗
Modified Source ↗
what is binary code ↗
Modified Source ↗
what is black hat hacking ↗
Modified Source ↗
what is blocklist ↗
Modified Source ↗
what is bluejacking ↗
Modified Source ↗
what is bluesnarfing bluetooth cybersecurity guide ↗
Modified Source ↗
what is boot sector ↗
Modified Source ↗
what is bot cybersecurity ↗
Modified Source ↗
what is botnet ↗
Modified Source ↗
what is brandjacking ↗
Modified Source ↗
what is bsod ↗
Modified Source ↗
what is bulletproof hosting ↗
Modified Source ↗
what is captcha cybersecurity guide ↗
Modified Source ↗
what is carding online fraud ↗
Modified Source ↗
what is chain of trust cybersecurity ↗
Modified Source ↗
what is click fraud ↗
Modified Source ↗
what is clickfake interview cybersecurity threat ↗
Modified Source ↗
what is clickfix ↗
Modified Source ↗
what is clickjacking ↗
Modified Source ↗
what is closed source software ↗
Modified Source ↗
what is cloud based ↗
Modified Source ↗
what is cloud compromise assessment ↗
Modified Source ↗
what is cloud computing ↗
Modified Source ↗
what is cloud data security ↗
Modified Source ↗
what is cloud incident response ↗
Modified Source ↗
what is cloud native ↗
Modified Source ↗
what is cloud workload protection ↗
Modified Source ↗
what is cold storage ↗
Modified Source ↗
what is command and control center ↗
Modified Source ↗
what is computer worm cybersecurity guide ↗
Modified Source ↗
what is conditional access ↗
Modified Source ↗
what is container security ↗
Modified Source ↗
what is containerization cybersecurity guide ↗
Modified Source ↗
what is conti ransomware ↗
Modified Source ↗
what is continuous monitoring ↗
Modified Source ↗
what is cookie logger ↗
Modified Source ↗
what is credential stuffing ↗
Modified Source ↗
what is credit card skimmer scam ↗
Modified Source ↗
what is crypto algorithim ↗
Modified Source ↗
what is crypto key ↗
Modified Source ↗
what is crypto malware cybersecurity guide ↗
Modified Source ↗
what is cryptocurrency ↗
Modified Source ↗
what is cryptor ↗
Modified Source ↗
what is cve ↗
Modified Source ↗
what is cvss ↗
Modified Source ↗
what is cyber threat ↗
Modified Source ↗
what is cybersecurity ↗
Modified Source ↗
what is cybersquatting ↗
Modified Source ↗
what is cyberweapon ↗
Modified Source ↗
what is dangling markup ↗
Modified Source ↗
what is dark ai cybersecurity threat guide ↗
Modified Source ↗
what is dark net cybersecurity guide ↗
Modified Source ↗
what is dark web monitoring ↗
Modified Source ↗
what is data compliance ↗
Modified Source ↗
what is data gravity ↗
Modified Source ↗
what is data logging ↗
Modified Source ↗
what is data obfuscation ↗
Modified Source ↗
what is data poisoning ↗
Modified Source ↗
what is ddos ↗
Modified Source ↗
what is debug logging ↗
Modified Source ↗
what is debug symbol ↗
Modified Source ↗
what is default deny ↗
Modified Source ↗
what is defense in depth ↗
Modified Source ↗
what is des ↗
Modified Source ↗
what is detection engineering ↗
Modified Source ↗
what is devsecops engineer ↗
Modified Source ↗
what is dictionary attack ↗
Modified Source ↗
what is digital certificate cybersecurity guide ↗
Modified Source ↗
what is dlp antivirus ↗
Modified Source ↗
what is dns poisoning cybersecurity guide ↗
Modified Source ↗
what is doh protocol ↗
Modified Source ↗
what is domain fronting ↗
Modified Source ↗
what is double tagging ↗
Modified Source ↗
what is downgrade attacks ↗
Modified Source ↗
what is doxware ↗
Modified Source ↗
what is dtls ↗
Modified Source ↗
what is emv ↗
Modified Source ↗
what is encryption ↗
Modified Source ↗
what is end to end encryption ↗
Modified Source ↗
what is enterprise solutions ↗
Modified Source ↗
ESPM ↗
Modified Source ↗
what is evil twin attack ↗
Modified Source ↗
what is file integrity monitoring ↗
Modified Source ↗
what is glitching cybersecurity attack ↗
Modified Source ↗
what is golden ticket attack ↗
Modified Source ↗
what is google cloud platform ↗
Modified Source ↗
what is hacklore ↗
Modified Source ↗
what is hacktivism ↗
Modified Source ↗
what is hash value ↗
Modified Source ↗
what is hashing cybersecurity ↗
Modified Source ↗
what is health insurance portability accountability act ↗
Modified Source ↗
what is heap spraying ↗
Modified Source ↗
what is heavens gate ↗
Modified Source ↗
what is honey token ↗
Modified Source ↗
what is honeypot ↗
Modified Source ↗
what is hooking ↗
Modified Source ↗
what is horizontal port scan ↗
Modified Source ↗
what is http2 ↗
Modified Source ↗
what is humint ↗
Modified Source ↗
what is hypervisor ↗
Modified Source ↗
what is iac scanning ↗
Modified Source ↗
what is identity resilience ↗
Modified Source ↗
what is identity segmentation ↗
Modified Source ↗
what is ids intrusion detection system ↗
Modified Source ↗
what is initial access cybersecurity threats ↗
Modified Source ↗
what is initialization vector ↗
Modified Source ↗
what is international revenue share fraud irsf ↗
Modified Source ↗
what is intrusion prevention system ↗
Modified Source ↗
what is ioa indicator of attack ↗
Modified Source ↗
what is ioc ↗
Modified Source ↗
what is iot cybersecurity ↗
Modified Source ↗
what is ipv6 benefits vs ipv4 ↗
Modified Source ↗
what is just in time access ↗
Modified Source ↗
what is kerberos ↗
Modified Source ↗
what is keystroke logging ↗
Modified Source ↗
what is kubernetes security best practices ↗
Modified Source ↗
what is lan id ↗
Modified Source ↗
what is lateral movement ↗
Modified Source ↗
what is layer 7 ↗
Modified Source ↗
what is log aggregation ↗
Modified Source ↗
what is log analysis ↗
Modified Source ↗
what is log parsing ↗
Modified Source ↗
what is logging level ↗
Modified Source ↗
what is long term evolution lte ↗
Modified Source ↗
what is mac flooding ↗
Modified Source ↗
what is magic number in cybersecurity ↗
Modified Source ↗
what is malspam ↗
Modified Source ↗
what is malware ↗
Modified Source ↗
what is malware analysis ↗
Modified Source ↗
what is managed security service providers ↗
Modified Source ↗
what is media server ↗
Modified Source ↗
what is mimikatz ↗
Modified Source ↗
what is mobile malware ↗
Modified Source ↗
what is negative digital footprint ↗
Modified Source ↗
what is network redirector ↗
Modified Source ↗
what is network segmentation ↗
Modified Source ↗
what is network traffic management ↗
Modified Source ↗
what is network tunneling ↗
Modified Source ↗
what is ngfw ips ↗
Modified Source ↗
what is ntlm ↗
Modified Source ↗
what is object linking embedding ↗
Modified Source ↗
what is observability in cybersecurity ↗
Modified Source ↗
what is on prem ↗
Modified Source ↗
what is one time passwords ↗
Modified Source ↗
what is open banking ↗
Modified Source ↗
what is openid connect ↗
Modified Source ↗
what is openssl ↗
Modified Source ↗
what is opentracing ↗
Modified Source ↗
what is osint ↗
Modified Source ↗
what is osquery endpoint security guide ↗
Modified Source ↗
what is packet capture ↗
Modified Source ↗
what is password cracking ↗
Modified Source ↗
what is pci dss ↗
Modified Source ↗
what is penetration testing ↗
Modified Source ↗
what is personally identifiable information ↗
Modified Source ↗
what is phishing and how does it affect your business ↗
Modified Source ↗
what is polymorphic virus ↗
Modified Source ↗
what is potentially unwanted application pua ↗
Modified Source ↗
what is pretexting cybersecurity guide ↗
Modified Source ↗
what is punycode cybersecurity guide ↗
Modified Source ↗
what is quantum cryptography ↗
Modified Source ↗
what is quishing ↗
Modified Source ↗
what is race condition ↗
Modified Source ↗
what is recovery point objective rpo ↗
Modified Source ↗
what is remote access ↗
Modified Source ↗
what is same origin policy ↗
Modified Source ↗
what is sandboxing ↗
Modified Source ↗
what is sase ↗
Modified Source ↗
what is scam llikely call ↗
Modified Source ↗
what is scareware ↗
Modified Source ↗
what is secret key authentication ↗
Modified Source ↗
what is secure socket layer ↗
Modified Source ↗
what is security by obscurity ↗
Modified Source ↗
what is security data lake ↗
Modified Source ↗
what is security misconfiguration ↗
Modified Source ↗
what is security operations center ↗
Modified Source ↗
what is security posture ↗
Modified Source ↗
what is security protocol ↗
Modified Source ↗
what is shadow data ↗
Modified Source ↗
what is simple mail transfer protocol ↗
Modified Source ↗
what is sip gateway ↗
Modified Source ↗
what is smishing ↗
Modified Source ↗
what is soa ↗
Modified Source ↗
what is soap protocol ↗
Modified Source ↗
what is soar ↗
Modified Source ↗
what is soc analyst ↗
Modified Source ↗
what is spam ↗
Modified Source ↗
what is spear phishing ↗
Modified Source ↗
what is ssh ↗
Modified Source ↗
what is ssl ↗
Modified Source ↗
what is ssl vnp ↗
Modified Source ↗
what is steganography ↗
Modified Source ↗
what is symmetric encryption algorithms ↗
Modified Source ↗
what is syn ↗
Modified Source ↗
what is tcp ip cybersecurity guide ↗
Modified Source ↗
what is telemetry in cybersecurity ↗
Modified Source ↗
what is traitorware ↗
Modified Source ↗
what is transport layer security encryption tls ↗
Modified Source ↗
what is trickbot ↗
Modified Source ↗
what is trojan bitcoin miner ↗
Modified Source ↗
what is typosquatting ↗
Modified Source ↗
what is udp ↗
Modified Source ↗
what is ueba ↗
Modified Source ↗
what is unauthorized access ↗
Modified Source ↗
what is use after free ↗
Modified Source ↗
what is vbs ↗
Modified Source ↗
what is virtual local area network vlan ↗
Modified Source ↗
what is vishing ↗
Modified Source ↗
what is vpn ↗
Modified Source ↗
what is watering hole attack ↗
Modified Source ↗
what is weaponization in cybersecurity ↗
Modified Source ↗
what is web shell ↗
Modified Source ↗
what is website defacement ↗
Modified Source ↗
what is website logging ↗
Modified Source ↗
what is zeus trojan ↗
Modified Source ↗
what is zip bomb ↗
Modified Source ↗
what is zombie botnet ↗
Modified Source ↗
whats a data backup ↗
Modified Source ↗
whats cross site scripting xss ↗
Modified Source ↗
whats digital signature ↗
Modified Source ↗
white team ↗
Modified Source ↗
who are cyber criminals ↗
Modified Source ↗
wiper attacks ↗
Modified Source ↗
wormgpt ↗
Modified Source ↗
xml external entity injection xxe ↗
Modified Source ↗
xsrf cross site request forgery explained ↗
Modified Source ↗
zero trust network access ↗
Modified Source ↗
what is a proxy ↗
Modified Source ↗
what is access control list ↗
Modified Source ↗
what is privilege escalation ↗
Modified Source ↗
what is zero trust security ↗
Modified Source ↗
cybersecurity 101 ↗
Modified Source ↗
whats digital signature ↗
Modified Source ↗
dont fall victim to cyber threats this holiday ↗
Modified Source ↗
secure the holiday spirit from cyber attacks ↗
Modified Source ↗
event id 4625 ↗
Modified Source ↗
what is siem ↗
Modified Source ↗
24 7 incident triage automated soc response ↗
Modified Source ↗
8 simple steps to harden hybrid identity security ↗
Modified Source ↗
a guide to itdr prioritization ↗
Modified Source ↗
all in one endpoint identity defense ↗
Modified Source ↗
arctic wolf alternatives ↗
Modified Source ↗
best cybersecurity awareness platforms ↗
Modified Source ↗
bitdefender alternatives ↗
Modified Source ↗
calculate itdr onboarding costs ↗
Modified Source ↗
calculate managed security service cost per device ↗
Modified Source ↗
compliance focused cybersecurity monitoring ↗
Modified Source ↗
crowdstrike alternatives ↗
Modified Source ↗
dark web monitoring platforms 2026 ↗
Modified Source ↗
data sovereignty cloud siem ↗
Modified Source ↗
enterprise grade security awareness training ↗
Modified Source ↗
espm cyber essentials certification ↗
Modified Source ↗
high risk user actions ↗
Modified Source ↗
how real time analytics reduce phishing risk ↗
Modified Source ↗
how to bake cake ↗
Modified Source ↗
how to integrate sat with hr lms systems ↗
Modified Source ↗
human risk management pricing models ↗
Modified Source ↗
human risk score platforms compared ↗
Modified Source ↗
human risk vendor managed services ↗
Modified Source ↗
integrating siem with edr and identity ↗
Modified Source ↗
itdr tools and continuous user baselining ↗
Modified Source ↗
kaseya alternatives ↗
Modified Source ↗
microsoft 365 hidden inbox rule detection ↗
Modified Source ↗
microsoft 365 itdr checklist 2025 ↗
Modified Source ↗
microsoft 365 phishing defense guide ↗
Modified Source ↗
red canary alternatives ↗
Modified Source ↗
sentinelone alternatives ↗
Modified Source ↗
threatlocker alternatives ↗
Modified Source ↗
Get a Demo ↗
Modified Source ↗
choose managed edr ↗
Modified Source ↗
gartner security summit ↗
Modified Source ↗
Education Cybersecurity Solutions That Keep Classrooms Running ↗
Modified Source ↗
How Does Phishing Affect Schools? ↗
Modified Source ↗
The Importance of K–12 Cybersecurity ↗
Modified Source ↗
Types of Cybercrime in the Banking Sector ↗
Modified Source ↗
What Is Financial Information Security? ↗
Modified Source ↗
financial services ↗
Modified Source ↗
healthcare compliance essentials ↗
Modified Source ↗
hospitals ↗
Modified Source ↗
insurance ↗
Modified Source ↗
data breach ↗
Modified Source ↗
ransomware in construction ↗
Modified Source ↗
ransomware in manufacturing ↗
Modified Source ↗
state and local government ↗
Modified Source ↗
utilities ↗
Modified Source ↗
opt out campaign ↗
Modified Source ↗
alliances ↗
Modified Source ↗
AI is changing cybersecurity. Here's how Huntress uses it. ↗
Modified Source ↗
Open Port Detection Solution ↗
Modified Source ↗
Persistent FootholdsDetectionSolution ↗
Modified Source ↗
Huntress Ransomware Canaries for Early Ransomware Detection ↗
Modified Source ↗
Managed ITDR for 24/7 Identity Threat Detection & Response ↗
Modified Source ↗
partner enablement ↗
Modified Source ↗
Content Authoring Software ↗
Modified Source ↗
onelogin ↗
Modified Source ↗
pricing ↗
Modified Source ↗
privacy policy ↗
Modified Source ↗
pto ↗
Modified Source ↗
resources ↗
Modified Source ↗
clickfix explained in 5 minutes ↗
Modified Source ↗
rsac2026 ↗
Modified Source ↗
cmmc ↗
Modified Source ↗
terms of use ↗
Modified Source ↗
adversary tactics ↗
Modified Source ↗
aadhaar data breach ↗
Modified Source ↗
accellion data breach ↗
Modified Source ↗
adobe data breach ↗
Modified Source ↗
alibaba data breach ↗
Modified Source ↗
anthem data breach ↗
Modified Source ↗
ashley madison data breach ↗
Modified Source ↗
bitly data breach ↗
Modified Source ↗
british airways data breach ↗
Modified Source ↗
bybit cryptocurrency exchange data breach ↗
Modified Source ↗
cam4 data breach ↗
Modified Source ↗
cambridge facebook scandal data breach ↗
Modified Source ↗
canva data breach ↗
Modified Source ↗
capital one data breach ↗
Modified Source ↗
cloudflare data breach ↗
Modified Source ↗
doordash data breach ↗
Modified Source ↗
dropbox data breach ↗
Modified Source ↗
dropbox password leak data breach ↗
Modified Source ↗
ebay data breach ↗
Modified Source ↗
equifax data breach ↗
Modified Source ↗
experian data breach ↗
Modified Source ↗
facebook user data breach ↗
Modified Source ↗
first american financial data breach ↗
Modified Source ↗
google plus data breach ↗
Modified Source ↗
grindr data breach ↗
Modified Source ↗
hacking team data breach ↗
Modified Source ↗
home depot data breach ↗
Modified Source ↗
intel data breach ↗
Modified Source ↗
irleaks data breach ↗
Modified Source ↗
ivanti mass zero day data breach ↗
Modified Source ↗
lumin pdf data breach ↗
Modified Source ↗
marriott data breach ↗
Modified Source ↗
medisecure data breach ↗
Modified Source ↗
microsoft customer support database data breach ↗
Modified Source ↗
myspace data breach ↗
Modified Source ↗
nasa data breach ↗
Modified Source ↗
national public data breach ↗
Modified Source ↗
neiman marcus data breach ↗
Modified Source ↗
neopets data breach ↗
Modified Source ↗
pinterest data breach ↗
Modified Source ↗
reddit data breach ↗
Modified Source ↗
robinhood data breach ↗
Modified Source ↗
samsung data breach ↗
Modified Source ↗
slack data breach ↗
Modified Source ↗
snapchat data breach ↗
Modified Source ↗
snowflake data breach ↗
Modified Source ↗
sony playstation data breach ↗
Modified Source ↗
spotify data breach ↗
Modified Source ↗
target data breach ↗
Modified Source ↗
telegram data breach ↗
Modified Source ↗
tfl transport for london data breach ↗
Modified Source ↗
ticketmaster data breach ↗
Modified Source ↗
tjmaxx data breach ↗
Modified Source ↗
tmobile data breach ↗
Modified Source ↗
twitch data breach ↗
Modified Source ↗
uber data breach ↗
Modified Source ↗
uk ministry of defence data breach ↗
Modified Source ↗
under armour myfitness pal data breach ↗
Modified Source ↗
us treasury data breach ↗
Modified Source ↗
weibo data breach ↗
Modified Source ↗
whatsapp data breach ↗
Modified Source ↗
yahoo data breach ↗
Modified Source ↗
zappos data breach ↗
Modified Source ↗
zoom data breach ↗
Modified Source ↗
acidrain ↗
Modified Source ↗
agent tesla ↗
Modified Source ↗
androm ↗
Modified Source ↗
asyncrat ↗
Modified Source ↗
autokms ↗
Modified Source ↗
bandok ↗
Modified Source ↗
bashlite ↗
Modified Source ↗
blackenergy ↗
Modified Source ↗
blackpos ↗
Modified Source ↗
blacksuit ↗
Modified Source ↗
blaster ↗
Modified Source ↗
boxter ↗
Modified Source ↗
bytefence ↗
Modified Source ↗
carbanak ↗
Modified Source ↗
cerber ↗
Modified Source ↗
cobalt strike ↗
Modified Source ↗
code red ↗
Modified Source ↗
coinminer ↗
Modified Source ↗
conficker malware ↗
Modified Source ↗
cryptonight malware ↗
Modified Source ↗
darkcomet ↗
Modified Source ↗
dorkbot ↗
Modified Source ↗
dridex ↗
Modified Source ↗
dtrack ↗
Modified Source ↗
duqu ↗
Modified Source ↗
egregor malware ↗
Modified Source ↗
emotet ↗
Modified Source ↗
expiro ↗
Modified Source ↗
flame malware ↗
Modified Source ↗
flashback ↗
Modified Source ↗
formbook ↗
Modified Source ↗
fusioncore ↗
Modified Source ↗
gamehack ↗
Modified Source ↗
gopher ↗
Modified Source ↗
gozi malware ↗
Modified Source ↗
hacktool ↗
Modified Source ↗
hacktool win32 crack malware ↗
Modified Source ↗
hacktool win32 keygen ↗
Modified Source ↗
icedid ↗
Modified Source ↗
iloveyou ↗
Modified Source ↗
irc bot ↗
Modified Source ↗
joker ↗
Modified Source ↗
khalesi malware ↗
Modified Source ↗
kinsing ↗
Modified Source ↗
kronos ↗
Modified Source ↗
kryptik ↗
Modified Source ↗
lavasoft web companion ↗
Modified Source ↗
lazagne ↗
Modified Source ↗
lumma stealer ↗
Modified Source ↗
malgent ↗
Modified Source ↗
matanbuchus ↗
Modified Source ↗
morto malware ↗
Modified Source ↗
mozi iot botnet ↗
Modified Source ↗
mydoom malware ↗
Modified Source ↗
mywebsearch malware ↗
Modified Source ↗
nanocore ↗
Modified Source ↗
neshta malware ↗
Modified Source ↗
nimda ↗
Modified Source ↗
no escape virus ↗
Modified Source ↗
notpetya ↗
Modified Source ↗
offercore ↗
Modified Source ↗
opencandy ↗
Modified Source ↗
pdfixers malware ↗
Modified Source ↗
pegasus malware ↗
Modified Source ↗
petya malware ↗
Modified Source ↗
phonzy ↗
Modified Source ↗
php webshell ↗
Modified Source ↗
plugx ↗
Modified Source ↗
poison ivy ↗
Modified Source ↗
predator ↗
Modified Source ↗
presenoker ↗
Modified Source ↗
pua win32 packunwan ↗
Modified Source ↗
pua win32 softcnapp ↗
Modified Source ↗
pua win32 vigua a malware ↗
Modified Source ↗
qq worm ↗
Modified Source ↗
regin ↗
Modified Source ↗
relevantknowledge ↗
Modified Source ↗
revshell ↗
Modified Source ↗
rhadamanthys ↗
Modified Source ↗
risepro ↗
Modified Source ↗
rootkit trojan ↗
Modified Source ↗
sality ↗
Modified Source ↗
slimware utilities ↗
Modified Source ↗
smokeloader ↗
Modified Source ↗
snake ↗
Modified Source ↗
softcnapp ↗
Modified Source ↗
spyeye malware ↗
Modified Source ↗
stealc ↗
Modified Source ↗
stuxnet malware ↗
Modified Source ↗
surtr malware ↗
Modified Source ↗
systembc ↗
Modified Source ↗
towelroot malware ↗
Modified Source ↗
triton ↗
Modified Source ↗
trojan downloader ↗
Modified Source ↗
trojan generic ↗
Modified Source ↗
trojan learn ↗
Modified Source ↗
trojan script wacatac ↗
Modified Source ↗
vidar ↗
Modified Source ↗
virut ↗
Modified Source ↗
wacapew ↗
Modified Source ↗
webcompanion ↗
Modified Source ↗
win32 induc ↗
Modified Source ↗
win32 xpaj ↗
Modified Source ↗
win64 malware gen ↗
Modified Source ↗
xworm ↗
Modified Source ↗
ytdownloader ↗
Modified Source ↗
zlob ↗
Modified Source ↗
zxx malware ↗
Modified Source ↗
blacksuit ransomware ↗
Modified Source ↗
colonial pipeline ransomware ↗
Modified Source ↗
egregor ↗
Modified Source ↗
halliburton ransomware ↗
Modified Source ↗
inc ransomware ↗
Modified Source ↗
indigo ransomware ↗
Modified Source ↗
lehigh valley health network ransomware ↗
Modified Source ↗
pepsi data breach ransomware 202 ↗
Modified Source ↗
phobos ↗
Modified Source ↗
royal mail ransomware ↗
Modified Source ↗
ryuk ransomware ↗
Modified Source ↗
steamship authority cyberattack ↗
Modified Source ↗
surtr ↗
Modified Source ↗
synnovis nhs uk ransomware attack ↗
Modified Source ↗
transnet ransomware ↗
Modified Source ↗
western digital cloud ransomware ↗
Modified Source ↗
yum brands data breach ↗
Modified Source ↗
zoll medical data breach ↗
Modified Source ↗
trojan horse malware ↗
Modified Source ↗
apprain cmf vulnerability ↗
Modified Source ↗
cross site scripting xss ↗
Modified Source ↗
cve 1999 0524 ↗
Modified Source ↗
cve 2000 0673 ↗
Modified Source ↗
cve 2006 0359 ↗
Modified Source ↗
cve 2014 0160 ↗
Modified Source ↗
cve 2014 6271 ↗
Modified Source ↗
cve 2016 2183 vulnerability ↗
Modified Source ↗
cve 2017 0143 ↗
Modified Source ↗
cve 2017 0144 ↗
Modified Source ↗
cve 2017 0199 ↗
Modified Source ↗
cve 2017 11882 ↗
Modified Source ↗
cve 2017 5638 ↗
Modified Source ↗
cve 2017 5715 ↗
Modified Source ↗
cve 2018 3646 ↗
Modified Source ↗
cve 2019 0708 ↗
Modified Source ↗
cve 2019 1040 ↗
Modified Source ↗
cve 2020 11022 ↗
Modified Source ↗
cve 2020 11023 ↗
Modified Source ↗
cve 2020 1472 ↗
Modified Source ↗
cve 2020 15368 ↗
Modified Source ↗
cve 2020 3259 ↗
Modified Source ↗
cve 2021 23840 vulnerability ↗
Modified Source ↗
cve 2021 30047 ↗
Modified Source ↗
cve 2021 3156 ↗
Modified Source ↗
cve 2021 4034 ↗
Modified Source ↗
cve 2021 41773 ↗
Modified Source ↗
cve 2021 44228 ↗
Modified Source ↗
cve 2021 45046 ↗
Modified Source ↗
cve 2022 1471 ↗
Modified Source ↗
cve 2022 29072 ↗
Modified Source ↗
cve 2022 30190 ↗
Modified Source ↗