Search result · source text not verified
Every AI-building team faces one question: can you trust what you're shipping? Snyk secures the code AI writes, the agents it runs, and the apps it builds.
Products
Snyk CodeSnyk Code is the fastest & most comprehensive SAST code vulnerability scanning and auto-fixing tool. Try Snyk’s code scanner solutions for free, or book a live demo.
Snyk Open SourceSnyk Open Source provides advanced software composition analysis (SCA) backed by industry-leading security and application intelligence.
Snyk ContainerSnyk Container Dev-first container security made simple Container and Kubernetes security solutions that help developers and DevOps find, prioritize, and fix vulnerabilities throughout the SDLC — before workloads hit production.
Snyk IaCSnyk Infrastructure as Code IaC security tools for Devs and DevOps Teams Find and fix misconfigurations in your infrastructure as code before they reach production.
Snyk SecretsSNYK SECRETS Stop the sprawl before it starts Block hardcoded credentials before they reach production with high-precision, ML-driven detection across your IDE, pull requests, and CI/CD — unified with the Snyk AI Security Platform.
Snyk AI Security PlatformThe Snyk AI Security Platform Snyk’s AI-native and agentic platform helps organizations secure and govern development to unleash productivity, reduce business risk, and accelerate software delivery for the age of AI.
DeepCode AIDeepCode AI code autofix empowers developers with efficient & accurate AppSec solutions.
Security IntelligenceSnyk’s security intelligence combines public sources, data from the developer community, proprietary expert research, machine learning, and human-in-the-loop AI.
EvoEvo gives teams continuous visibility, governance, testing, and real-time control across AI development and AI-native apps, helping organizations scale AI safely without slowing innovation.
Evo Agentic Development SecurityEvo Agentic Development Security (ADS) secures what agents use, what they do, and what they generate — so you can adopt AI safely and move at AI speed without losing control.
Evo AI-SPMEvo AI-SPM makes AI visible, governable, and enforceable.
Evo Agentic AppSecEvo Agentic AppSec puts a team of security agents next to every engineer, running the entire AppSec program end to end: understand, find, fix, and verify at the speed AI now builds and attacks software, with your team owning the bar.
Code CheckerAI-powered Code Checker Scan your code before your next PR commit, identify vulnerabilities, and get alerts of critical bugs using our free code checker — powered by Snyk Code.
No matching products or features.
Customer feedback
Search result · source text not verified
Snyk laid off up to 30% of their staff today
Search result · source text not verified
Opinion: Snyk vs Checkmarx One
Search result · source text not verified
Implementating Snyk into the Org
Search result · source text not verified
Snyk SE interview
Search result · source text not verified
Anyone working/worked at Snyk? : r/techsales
I’m in the later stages of the process for an Enterprise role. RepVue and Glassdoor are pretty positive but would like to get some first hand thoughts.
Search result · source text not verified
Is Snyk worth the price? : r/devops
We're looking to improve security and Snyk looks like the industry leader in for SAST, vulnerabilities in images, IaC analysis.
Search result · source text not verified
Anyone else tired of juggling SonarQube, Snyk, and ...
Our setup has become ridiculous. SonarQube runs nightly, Snyk yells about vulnerabilities once a week, and reviewers manually check for style and logic. ...
Search result · source text not verified
Snyk Reviews 2026: Details, Pricing, & Features
In CI, we run snyk test and snyk code test, and the IDE plugin catches many issues before a pull request even exists. That combination has done ...
Search result · source text not verified
Snyk Reviews from Real Users
The Snyk Code IDE plugin is something that really works very well and brings out the true shift left story by providing very accurate findings and equally good ...
Search result · source text not verified
Snyk Products | Read 138 Reviews on ...
Snyk has been rated 4.5 stars by 138 verified reviews on G2. Explore all ... In CI, we run snyk test and snyk code test, and the IDE plugin catches ...
Search result · source text not verified
Snyk Code Reviews & Ratings 2026 | Gartner Peer Insights
I've had a very positive experience with Snyk Code overall, the platform is easy to integrate into existing development workflows and provides actionable ...
Search result · source text not verified
AWS BugBust
I looked into Snyk Code, but it's mad expensive. vips7L on June 25, 2021 | parent | next [–]. If you want free sonarlint is good for every ...
No feedback found.
Marketing & Ads
GoogleSnyk Limited
Original ad ↗ First shown May 18, 2026 · Last shown Nov 11, 2026
Landing page unavailable: the ad source did not supply a destination URL.
GoogleSnyk Limited
Original ad ↗ First shown Sep 19, 2025 · Last shown Nov 11, 2026
Landing page unavailable: the ad source did not supply a destination URL.
LinkedInSnyk
Original ad ↗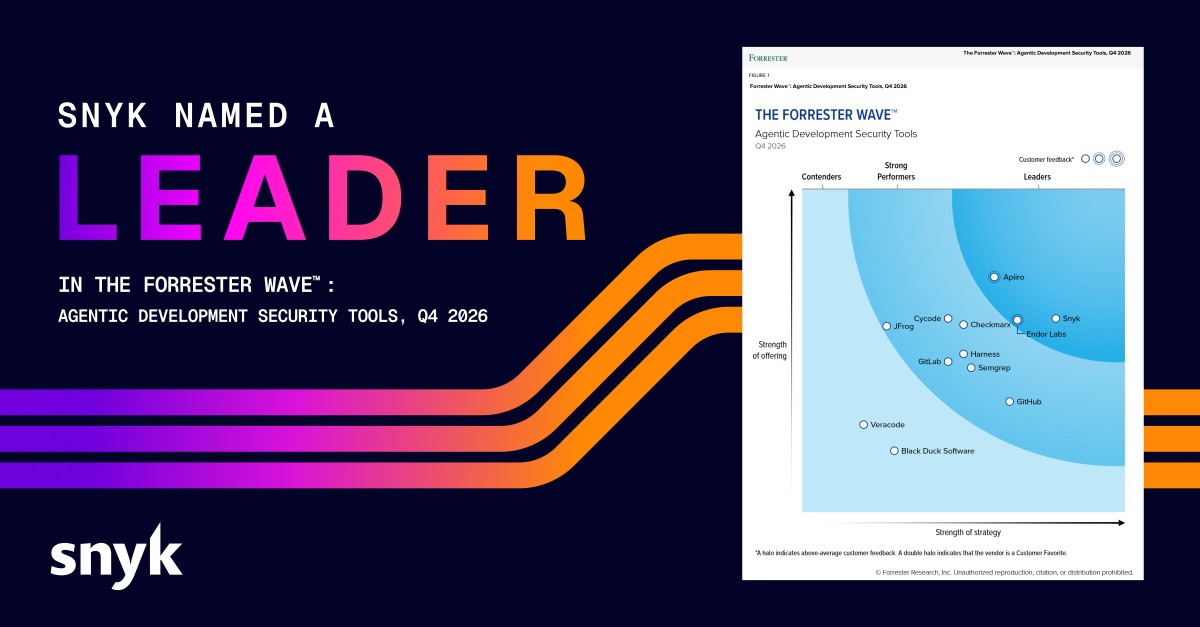
Forrester says AI coding agents are “moving from developer assistants to active participants in development workflows.” Snyk has been named a Leader in The Forrester Wave™: Agentic Development Security Tools, Q4 2026, with the highest score in the Strategy category. We believe that reflects our focus on securing software where it is created, which now includes the agents creating it. Get the complimentary report: https://vist.ly/5rdgr
Landing page unavailable: the ad source did not supply a destination URL.
GoogleSnyk Limited
Original ad ↗ First shown Jun 22, 2026 · Last shown Nov 10, 2026
Landing page unavailable: the ad source did not supply a destination URL.
GoogleSnyk Limited
Original ad ↗ First shown Jun 22, 2026 · Last shown Nov 10, 2026
Landing page unavailable: the ad source did not supply a destination URL.
GoogleSnyk Limited
Original ad ↗ First shown Jun 22, 2026 · Last shown Nov 10, 2026
Landing page unavailable: the ad source did not supply a destination URL.
GoogleSnyk Limited
Original ad ↗ First shown May 18, 2026 · Last shown Nov 10, 2026
Landing page unavailable: the ad source did not supply a destination URL.
LinkedInSnyk
Original ad ↗
Evo catches what agents miss.
Your agents write code faster than your team can check it. Evo reviews every commit for the vulnerabilities that slip through.
Learn more
Landing page unavailable: the ad source did not supply a destination URL.
GoogleSnyk Limited
Original ad ↗First shown May 18, 2026 · Last shown Nov 10, 2026Landing page unavailable: the ad source did not supply a destination URL.
GoogleSnyk Limited
Original ad ↗Risks of AI Generated Code
Almost half of AI-generated code is vulnerable. Learn how to secure what ships.
First shown Jun 23, 2026 · Last shown Nov 10, 2026Landing page unavailable: the ad source did not supply a destination URL.
GoogleSnyk Limited
Original ad ↗ First shown Feb 25, 2026 · Last shown Nov 10, 2026
Landing page unavailable: the ad source did not supply a destination URL.
GoogleSnyk Limited
Original ad ↗ First shown May 18, 2026 · Last shown Nov 10, 2026
Landing page unavailable: the ad source did not supply a destination URL.
LinkedInSnyk
Original ad ↗
Evo Agentic AppSec: AI for Application Security
Agents write code faster than security teams can triage it. New critical and high-severity issues across Snyk customers grew 10x in the past year. Today we launched Evo Agentic AppSec: a team of security agents that finds, fixes, and blocks vulnerabilities at the speed agents write code, with every result verified independently of the agent that produced it. Evo Code Scanning Agent catches the access control and authentication flaws pattern-matching misses. Evo Dependency Firewall blocks malicious and slopsquatted packages at install. Evo Agentic Security Review threat-models a full repository and returns evidence-backed findings. Evo Remediation Agent ships fixes you can merge: 90% of the time on open source dependency issues, versus 59.6% for an LLM alone. And Evo Secrets Detection catches leaked credentials from IDE to CI. Read the full announcement: https://lnkd.in/en-YET-s
First shown Oct 16, 2026 · Last shown Oct 23, 2026
LinkedInSnyk
Original ad ↗
Still deciding? Evo catches it.
You already know 150,000+ AI agents are coming by 2028. The question is whether Evo is catching what yours ship.
Learn more
Landing page unavailable: the ad source did not supply a destination URL.
LinkedInSnyk
Original ad ↗
Still deciding? Evo catches it.
You already know 150,000+ AI agents are coming by 2028. The question is whether Evo is catching what yours ship.
Learn more
Landing page unavailable: the ad source did not supply a destination URL.
LinkedInManoj Nair
Original ad ↗
The AI hurricane is here. Debating its speed will not “weatherproof” the software we already run or protect against the attackers who aren’t slowing down. Creation moved to machine speed. Validation did not. Meanwhile, agents are writing code, choosing tools, and acting in production—and attackers can exploit that growing exposure with AI of their own. Dario & Sam’s call for independent lab evaluators and George Kurtz’s answer is the operational one: the frontier moves at whatever speed it moves, but the rest of the world does not slow down. Both are right. But we have to take it one layer upstream. I’d extend that responsibility into development. ❓Who governs the agents doing the writing? ❓Who checks the tools, skills and MCP servers they trust? ❓Who independently validates the code, and the fixes they ship? The system creating a change cannot be its own sole validator. We need independently executed tests, production evidence, and validation controls the generating agent cannot alter. And defenders need the means to act. Open models, shared intelligence, and supported open-source maintainers belong inside the safety architecture. Continuous defense must be affordable and broadly accessible. ✅ Secure at inception. ✅ Enforce at runtime. ✅ Validate independently. Read my in-depth thoughts and recommendations here, along with the questions leaders should ask their teams (or their agents) now. https://lnkd.in/eiyiuxuj The strongest movement is still Open Source and Open Models. The Security companies are Allied. The Defenders are still standing strong. Open. Allied. Still Standing - thats the mantra to focus on the most important task right now and cut through the opera.
First shown Sep 15, 2026 · Last shown Sep 23, 2026
LinkedInSnyk
Original ad ↗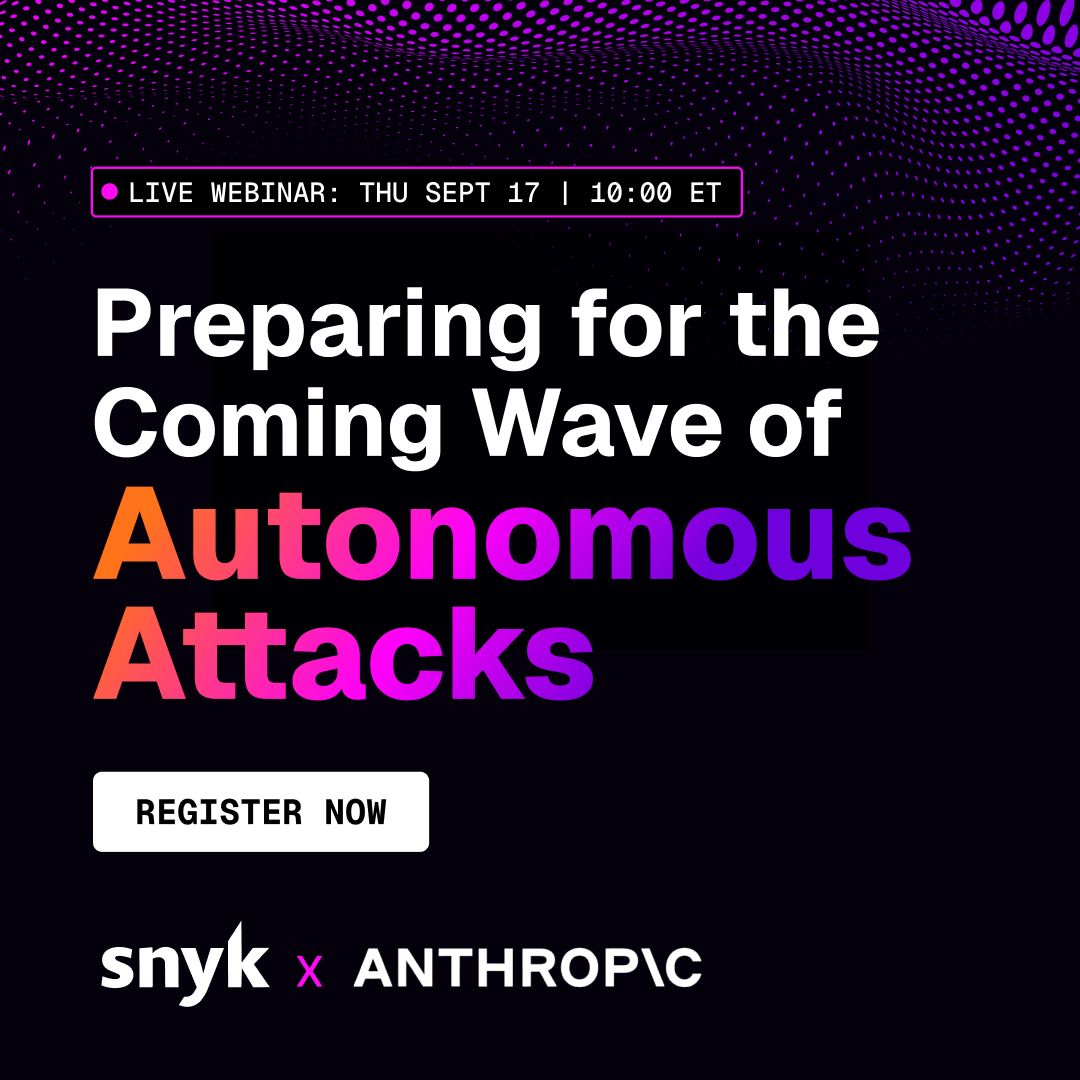
Live Webinar, Thu 17 Sep, 10:00am ET
Autonomous, AI-driven attacks move faster than most security teams, or their vendors, can respond. Snyk and Anthropic are answering the question live: how do you defend against it? Register for the September 17 webinar now.
Register
Landing page unavailable: the ad source did not supply a destination URL.
LinkedInSnyk
Original ad ↗
Evo catches what agents miss.
Your agents write code faster than your team can check it. Evo reviews every commit for the vulnerabilities that slip through.
Learn more
Landing page unavailable: the ad source did not supply a destination URL.
New pages
Snyk Named a Leader in Agentic Development Security Tools by Independent Research Firm ↗
Snyk Launches Evo Agentic AppSec, Redefining Traditional AppSec With a Team of Security Agents ↗
As AI Risk Scales and Vulnerabilities Compound, Evo by Snyk Reaches 60% of New Deal Volume ↗
Snyk Launches Evo Continuous Offensive Security to Protect Enterprises Against Autonomous AI Attacks ↗
Enterprises Are Blind to Two-Thirds of Their Own AI Attack Surface. The Blind Spot Is Growing Fast. ↗
Modified Source ↗
Snyk vs Wiz ↗
Modified Source ↗
snyk vs wiz ↗
Modified Source ↗
snyk vs wiz ↗
Modified Source ↗
snyk vs wiz ↗
Modified Source ↗
snyk vs wiz ↗
Modified Source ↗
Snyk vs Checkmarx ↗
Modified Source ↗
snyk vs checkmarx ↗
Modified Source ↗
snyk vs checkmarx ↗
Modified Source ↗
snyk vs checkmarx ↗
Modified Source ↗
snyk vs checkmarx ↗
Modified Source ↗
Snyk vs Veracode ↗
Modified Source ↗
snyk vs veracode ↗
Modified Source ↗
snyk vs veracode ↗
Modified Source ↗
snyk vs veracode ↗
Modified Source ↗
snyk vs veracode ↗
Modified Source ↗
a beginners guide to visually understanding mcp architecture ↗
Modified Source ↗
risk based vulnerability management ↗
Modified Source ↗
code review ↗
Modified Source ↗
Say Yes To MCP, Safely A Guide For Governing AI Coding Agents With Evo ADS ↗
Modified Source ↗
our webinars ↗
Modified Source ↗
devoxx4kids empowering young java developers and creating future industry stars ↗
Modified Source ↗
manifold ↗
Modified Source ↗
IDE-Plugins für sichere Entwicklung ↗
Modified Source ↗
Plugins para IDEs que permiten desarrollar de forma segura ↗
Modified Source ↗
Des plugins IDE pour un développement sécurisé ↗
Modified Source ↗
セキュアな開発を実現するIDEプラグイン ↗
Modified Source ↗
IDE plugins for secure development ↗
Modified Source ↗
ide plugins ↗
Modified Source ↗
snyk cli ↗
Modified Source ↗
snyk cli ↗
Modified Source ↗
snyk cli ↗
Modified Source ↗
snyk cli ↗
Modified Source ↗
Snyk CLI ↗
Modified Source ↗
snyk cli ↗
Modified Source ↗
infrastructure as code security ↗
Modified Source ↗
infrastructure as code security ↗
Modified Source ↗
infrastructure as code security ↗
Modified Source ↗
infrastructure as code security ↗
Modified Source ↗
IaC security tools for Devs and DevOps Teams ↗
Modified Source ↗
infrastructure as code security ↗
Modified Source ↗
open source security management ↗
Modified Source ↗
open source security management ↗
Modified Source ↗
open source security management ↗
Modified Source ↗
open source security management ↗
Open source risk management made for developers ↗
Modified Source ↗
open source security management ↗
Modified Source ↗
git repository security ↗
Modified Source ↗
snyk javascript security ↗
Modified Source ↗
snyk java security ↗
Modified Source ↗
snyk python security ↗
Modified Source ↗
ci cd pipeline security ↗
Modified Source ↗
Snyk vs GitHub Advanced Security ↗
Modified Source ↗
github vs snyk ↗
Modified Source ↗
github vs snyk ↗
Modified Source ↗
github vs snyk ↗
Modified Source ↗
github vs snyk ↗
Modified Source ↗
tapp ↗
Modified Source ↗
tapp ↗
Modified Source ↗
tapp ↗
Modified Source ↗
tapp ↗
Modified Source ↗
tapp ↗
Modified Source ↗
tapp ↗
Modified Source ↗
Secure how software is built in the age of AI agents ↗
Modified Source ↗
Snyk vs Black Duck ↗
Modified Source ↗
snyk vs blackduck ↗
Modified Source ↗
snyk vs blackduck ↗
Modified Source ↗
snyk vs blackduck ↗
Modified Source ↗
snyk vs blackduck ↗
Modified Source ↗
resource library ↗
Modified Source ↗
resource library ↗
Modified Source ↗
resource library ↗
Modified Source ↗
resource library ↗
Modified Source ↗
resource library ↗
Modified Source ↗
Explore all resources ↗
Modified Source ↗
news ↗
Modified Source ↗
news ↗
Modified Source ↗
news ↗
Modified Source ↗
news ↗
Modified Source ↗
Newsroom ↗
Modified Source ↗
news ↗
Modified Source ↗
Explore all blogs ↗
Modified Source ↗
blog ↗
Modified Source ↗
blog ↗
Modified Source ↗
blog ↗
Modified Source ↗
blog ↗
Modified Source ↗
blog ↗
Modified Source ↗
secure sdlc best practices ↗
Modified Source ↗
docker hub authentication 2fa ↗
Modified Source ↗
building vue 3 components tailwind css ↗
Modified Source ↗
software supply chain security ↗
Modified Source ↗
moq package exfiltrates user emails ↗
Modified Source ↗
generate sbom javascript node js applications ↗
Modified Source ↗
automated code review ↗
Modified Source ↗
application security best practices ↗
Modified Source ↗
verdaccio project spotlight ↗
Modified Source ↗
ai hallucinations ↗
Modified Source ↗
ai hallucinations ↗
Modified Source ↗
ai hallucinations ↗
Modified Source ↗
ai hallucinations ↗
Modified Source ↗
ai hallucinations ↗
Modified Source ↗
remediating vulnerabilities ↗
Modified Source ↗
container scanning ↗
Modified Source ↗
mastering python virtual environments ↗
Modified Source ↗
jinja2 xss vulnerability ↗
Modified Source ↗
secure python flask applications ↗
Modified Source ↗
getting started php static analysis 2024 ↗
Modified Source ↗
10 modern node js runtime features ↗
Modified Source ↗
how to avoid ssrf vulnerability in go applications ↗
Modified Source ↗
promise queues concurrent tasks deno ↗
Modified Source ↗
minimizing false positives enhancing security efficiency ↗
Modified Source ↗
next level ci cd embedding security in your devops journey ↗
Modified Source ↗
python pickle poisoning and backdooring pth files ↗
Modified Source ↗
php code security ↗
Modified Source ↗
decoding sql injection strategies for secure web applications ↗
Modified Source ↗
guardians of the gateway how api security testing tools protect your data ↗
Modified Source ↗
beyond the basics advanced insights into xss vulnerabilities ↗
Modified Source ↗
smarter appsec how ai is revolutionizing web application scanning ↗
Modified Source ↗
nine docker pro tips node js developers ↗
Modified Source ↗
phishing campaign leveraging the npm ecosystem ↗
Modified Source ↗
deployment options ↗
Modified Source ↗
deployment options ↗
Modified Source ↗
deployment options ↗
Modified Source ↗
deployment options ↗
Modified Source ↗
Deployment Options ↗
Modified Source ↗
deployment options ↗
Modified Source ↗
typescript ↗
Modified Source ↗
typescript ↗
Modified Source ↗
typescript ↗
Modified Source ↗
typescript ↗
Modified Source ↗
typescript ↗
Modified Source ↗
website scanner ↗
Modified Source ↗
website scanner ↗
Modified Source ↗
website scanner ↗
Modified Source ↗
website scanner ↗
Modified Source ↗
ethical hacking resources ↗
Modified Source ↗
ethical hacking resources ↗
Modified Source ↗
ethical hacking resources ↗
Modified Source ↗
ethical hacking resources ↗
Modified Source ↗
AI-powered Code Checker ↗
Modified Source ↗
code checker ↗
Modified Source ↗
code checker ↗
Modified Source ↗
code checker ↗
Modified Source ↗
code checker ↗
Modified Source ↗
code checker ↗
Modified Source ↗
go ↗
Modified Source ↗
go ↗
Modified Source ↗
go ↗
Modified Source ↗
go ↗
Modified Source ↗
go ↗
Modified Source ↗
java ↗
Modified Source ↗
java ↗
Modified Source ↗
java ↗
Modified Source ↗
java ↗
Modified Source ↗
java ↗
Modified Source ↗
sbom security ↗
Modified Source ↗
sbom security ↗
Modified Source ↗
sbom security ↗
Modified Source ↗
sbom security ↗
Modified Source ↗
javascript ↗
Modified Source ↗
javascript ↗
Modified Source ↗
javascript ↗
Modified Source ↗
javascript ↗
Modified Source ↗
javascript ↗
Modified Source ↗
php ↗
Modified Source ↗
php ↗
Modified Source ↗
php ↗
Modified Source ↗
php ↗
Modified Source ↗
php ↗
Modified Source ↗
ruby ↗
Modified Source ↗
ruby ↗
Modified Source ↗
ruby ↗
Modified Source ↗
ruby ↗
Modified Source ↗
ruby ↗
Modified Source ↗
python ↗
Modified Source ↗
python ↗
Modified Source ↗
python ↗
Modified Source ↗
python ↗
Modified Source ↗
python ↗
Modified Source ↗
de ↗
Modified Source ↗
es ↗
Modified Source ↗
fr ↗
Modified Source ↗
jp ↗
Modified Source ↗
pt BR ↗
Modified Source ↗
articles ↗
Modified Source ↗
Snyk ' s Podcasts ↗
Modified Source ↗
videos ↗
Modified Source ↗
videos ↗
Modified Source ↗
videos ↗
Modified Source ↗
videos ↗
Modified Source ↗
videos ↗
Modified Source ↗
videos ↗
Modified Source ↗
Case Studies Check out our customer stories and stats ↗
Modified Source ↗
case studies ↗
Modified Source ↗
case studies ↗
Modified Source ↗
case studies ↗
Modified Source ↗
case studies ↗
Modified Source ↗
case studies ↗
Modified Source ↗
Read more ↗
Modified Source ↗
sergey gerasimenko ↗
Modified Source ↗
brendan hann ↗
Modified Source ↗
Agentic AppSec: Software Development Went Agentic. Security Didn’t. ↗
Modified Source ↗
gabija pasiunaite ↗
Modified Source ↗
ryan mcmorrow ↗
Modified Source ↗
VulnBump: Can AI Agents Fix Vulnerable Dependencies Without Breaking the Build? ↗
Modified Source ↗
Evo by Snyk ↗
Modified Source ↗
snyk windsurf ↗
Modified Source ↗
snyk kiro ↗
Modified Source ↗
snyk factory ↗
Modified Source ↗
Learn More ↗
Modified Source ↗
cognition ↗
Modified Source ↗
Learn More ↗
Modified Source ↗
plans ↗
Modified Source ↗
plans ↗
Modified Source ↗
plans ↗
Modified Source ↗
plans ↗
Modified Source ↗
Pricing ↗
Modified Source ↗
plans ↗
Modified Source ↗
snyk track ↗
Modified Source ↗
security culture sessions ↗
Modified Source ↗
partner sessions ↗
Modified Source ↗
open source security sessions ↗
Modified Source ↗
ai security sessions ↗
Modified Source ↗
services ↗
Modified Source ↗
services ↗
Modified Source ↗
services ↗
Modified Source ↗
services ↗
Modified Source ↗
services ↗
Modified Source ↗
Our Services Maximize your AppSec ROI ↗
Modified Source ↗
php patches critical unauthenticated rces ↗
Modified Source ↗
mainstage sessions ↗
Modified Source ↗
Careers Join Snyk today ↗
Modified Source ↗
careers ↗
Modified Source ↗
careers ↗
Modified Source ↗
careers ↗
Modified Source ↗
careers ↗
Modified Source ↗
careers ↗
Modified Source ↗
integrations ↗
Modified Source ↗
integrations ↗
Modified Source ↗
integrations ↗
Modified Source ↗
Snyk integrations ↗
Modified Source ↗
integrations ↗
Modified Source ↗
integrations ↗
Modified Source ↗
ai vibe check ↗
Modified Source ↗
black hat asia customer panel recap ↗
Modified Source ↗
shopback ↗
Modified Source ↗
shopback ↗
Modified Source ↗
shopback ↗
Modified Source ↗
shopback ↗
Modified Source ↗
shopback ↗
Modified Source ↗
pomelo ↗
Modified Source ↗
mollie ↗
Modified Source ↗
telenor ↗
Modified Source ↗
skyscanner ↗
Modified Source ↗
skyscanner ↗
Modified Source ↗
skyscanner ↗
Modified Source ↗
skyscanner ↗
Modified Source ↗
depop ↗
Modified Source ↗
flo health ↗
Modified Source ↗
blue prism ↗
Modified Source ↗
origo ↗
Modified Source ↗
Read case study ↗
Modified Source ↗
panther labs ↗
Modified Source ↗
panther labs ↗
Modified Source ↗
panther labs ↗
Modified Source ↗
panther labs ↗
Modified Source ↗
Read case study ↗
Modified Source ↗
mongodb ↗
Modified Source ↗
mongodb ↗
Modified Source ↗
mongodb ↗
Modified Source ↗
Read case study ↗
Modified Source ↗
natera ↗
Modified Source ↗
natera ↗
Modified Source ↗
natera ↗
Modified Source ↗
natera ↗
Modified Source ↗
acuity knowledge partners ↗
Modified Source ↗
form 3 ↗
Modified Source ↗
coveo 2 ↗
Modified Source ↗
salesforce ↗
Modified Source ↗
salesforce ↗
Modified Source ↗
salesforce ↗
Modified Source ↗
salesforce ↗
Modified Source ↗
salesforce ↗
Modified Source ↗
asurion ↗
Modified Source ↗
overstock ↗
Modified Source ↗
helvetia ↗
Modified Source ↗
pearson ↗
Modified Source ↗
lunar ↗
Modified Source ↗
coveo ↗
Modified Source ↗
auth0 ↗
Modified Source ↗
how onna uses snyk and sysdig to secure the sdlc ↗
Modified Source ↗
Improving developer experience with security tools at Pinterest ↗
Modified Source ↗
liveramp used snyk to remediate log4shell ↗
Modified Source ↗
surveymonkey developer security hypergrowth ↗
Modified Source ↗
surveymonkey developer security hypergrowth ↗
Modified Source ↗
surveymonkey developer security hypergrowth ↗
Modified Source ↗
surveymonkey developer security hypergrowth ↗
Modified Source ↗
lunar shifted security left building cloud native bank ↗
Modified Source ↗
datto developer first security snyk ↗
Modified Source ↗
dun bradstreet shutterstock security champions programs ↗
Modified Source ↗
securing cloud native applications activecampaigns vp information security provides perspective ↗
Modified Source ↗
snyk chats with shutterstock about building a devsecops culture ↗
Modified Source ↗
snyk watcher keep snyk in sync ↗
Modified Source ↗
modern security leader spotlight marcin hoppe senior manager product security at auth0 ↗
Modified Source ↗
dfds ↗
Modified Source ↗
dfds ↗
Modified Source ↗
dfds ↗
Modified Source ↗
dfds ↗
Modified Source ↗
dfds ↗
Modified Source ↗
technologyone ↗
Modified Source ↗
Read case study ↗
Modified Source ↗
php2shell where next one will show up first ↗
Modified Source ↗
ricardo alves ↗
Modified Source ↗
procurement ↗
Modified Source ↗
log4j vulnerability resources ↗
Modified Source ↗
board ↗
Modified Source ↗
board ↗
Modified Source ↗
board ↗
Modified Source ↗
board ↗
Modified Source ↗
board ↗
Modified Source ↗
board ↗
Modified Source ↗
security leaders ↗
Modified Source ↗
security leaders ↗
Modified Source ↗
security leaders ↗
Modified Source ↗
security leaders ↗
Modified Source ↗
security leaders ↗
Modified Source ↗
security leaders ↗
Modified Source ↗
Learn More ↗
Modified Source ↗
partners ↗
Modified Source ↗
partners ↗
Modified Source ↗
partners ↗
Modified Source ↗
partners ↗
Modified Source ↗
Our Partners Bringing business class security with partners ↗
Modified Source ↗
partners ↗
Modified Source ↗
codex ↗
Modified Source ↗
Snyk customer resources ↗
Modified Source ↗
customer resources ↗
Modified Source ↗
customer resources ↗
Modified Source ↗
customer resources ↗
Modified Source ↗
customer resources ↗
Modified Source ↗
customer resources ↗
Modified Source ↗
About Snyk ↗
Modified Source ↗
about ↗
Modified Source ↗
about ↗
Modified Source ↗
about ↗
Modified Source ↗
about ↗
Modified Source ↗
about ↗
Modified Source ↗
open source ↗
Modified Source ↗
Leadership Meet our leaders ↗
Modified Source ↗
leadership ↗
Modified Source ↗
leadership ↗
Modified Source ↗
leadership ↗
Modified Source ↗
leadership ↗
Modified Source ↗
leadership ↗
Modified Source ↗
security ↗
Modified Source ↗
security ↗
Modified Source ↗
security ↗
Modified Source ↗
security ↗
Modified Source ↗
snyk unfiltered customer summit ↗
Modified Source ↗
Contact team ↗
Modified Source ↗
Get in touch ↗
Modified Source ↗
contact us ↗
Modified Source ↗
contact us ↗
Modified Source ↗
contact us ↗
Modified Source ↗
contact us ↗
Modified Source ↗
contact us ↗
Modified Source ↗
daikin industries introduces vulnerability management tool snyk ↗
Modified Source ↗
daikin industries introduces vulnerability management tool snyk ↗
Modified Source ↗
daikin industries introduces vulnerability management tool snyk ↗
Modified Source ↗
daikin industries introduces vulnerability management tool snyk ↗
Modified Source ↗
daikin industries introduces vulnerability management tool snyk ↗
Modified Source ↗
daikin industries introduces vulnerability management tool snyk ↗
Modified Source ↗
snyk top 10 ↗
Modified Source ↗
snyk top 10 ↗
Modified Source ↗
snyk top 10 ↗
Modified Source ↗
snyk top 10 ↗
Modified Source ↗
report a vulnerability ↗
Modified Source ↗
benefits sast dast together ↗
Modified Source ↗
frontier models vulnerabilities attacker chains ↗
Modified Source ↗
schedule a demo ↗
Modified Source ↗
schedule a demo ↗
Modified Source ↗
schedule a demo ↗
Modified Source ↗
schedule a demo ↗
Modified Source ↗
schedule a demo ↗
Modified Source ↗
See Snyk in action ↗
Modified Source ↗
gareth rushgrove ↗
Modified Source ↗
write secure kubernetes configuration with help from snyk ↗
Modified Source ↗
immutable inf networks ↗
Modified Source ↗
sql injection orm vulnerabilities ↗
Modified Source ↗
guide to emacs ↗
Modified Source ↗
node js timing attack ccc ctf ↗
Modified Source ↗
10 reasons to use https ↗
Modified Source ↗
publishing malicious packages ↗
Modified Source ↗
leaked credentials in packages ↗
Modified Source ↗
architecting a serverless web application in aws ↗
Modified Source ↗
exploiting buffer ↗
Modified Source ↗
whats an npm dependency ↗
Modified Source ↗
tackling the new npm3 dependency tree ↗
Modified Source ↗
marked xss vulnerability ↗
Modified Source ↗
engineering and basketball ↗
Modified Source ↗
public github repo monitoring ↗
Modified Source ↗
snyk launch ↗
Modified Source ↗
nodejs attack tree modelling ↗
Modified Source ↗
devops and open source security ↗
Modified Source ↗
safe imagemagick for node ↗
Modified Source ↗
https breaking through ↗
Modified Source ↗
out of beta ↗
Modified Source ↗
snyk partners with bithound ↗
Modified Source ↗
github integration ↗
Modified Source ↗
using es2015 proxy for fun and profit ↗
Modified Source ↗
five ways to get nodejs vulnerability alerts ↗
Modified Source ↗
yarn is micro secure ↗
Modified Source ↗
fixing ejs rce vuln ↗
Modified Source ↗
slack integration ↗
Modified Source ↗
the secure developer podcast ↗
Modified Source ↗
mongodb hack and secure defaults ↗
Modified Source ↗
diagnosing and fixing memory leaks in python ↗
Modified Source ↗
announcing snyk for bitbucket pipelines ↗
Modified Source ↗
differences in version handling gems and npm ↗
Modified Source ↗
vsts snyk interview with jesse houwing ↗
Modified Source ↗
snyk cli for ruby ↗
Modified Source ↗
launching serverless snyk ↗
Modified Source ↗
welcome ruby users ↗
Modified Source ↗
a brief history ↗
Modified Source ↗
redos and catastrophic backtracking ↗
Modified Source ↗
the secure developer security dev tools ↗
Modified Source ↗
serverless security implications from infra to owasp ↗
Modified Source ↗
requiring authentication ↗
Modified Source ↗
type manipulation ↗
Modified Source ↗
understanding responsible disclosures ↗
Modified Source ↗
voltos and snyk ↗
Modified Source ↗
77 percent of sites use vulnerable js libraries ↗
Modified Source ↗
pkgbot intro ↗
Modified Source ↗
building the gulp snyk plugin ↗
Modified Source ↗
nokogiri xxe vulnerabilities ↗
Modified Source ↗
xray integration ↗
Modified Source ↗
owasp top 10 breaches ↗
Modified Source ↗
snyk projects now free ↗
Modified Source ↗
known vulnerabilities in javascript ↗
Modified Source ↗
vscode interview with peter benjamin ↗
Modified Source ↗
high severity vulnerability qs ↗
Modified Source ↗
xss attacks the next wave ↗
Modified Source ↗
launching snyk for serverless ↗
Modified Source ↗
maven support is here ↗
Modified Source ↗
snyk and atlassian ↗
Modified Source ↗
bitbucket server beta ↗
Modified Source ↗
equifax breach vulnerable open source libraries ↗
Modified Source ↗
announcing cloud foundry support at cf summit ↗
Modified Source ↗
fserverless security at serverless conf ↗
Modified Source ↗
snyk is on govuk marketplace ↗
Modified Source ↗
snyk enterprise launch ↗
Modified Source ↗
python 2 vs 3 security differences ↗
Modified Source ↗
snyk for gradle scala python ↗
Modified Source ↗
getting the most out of snyk test ↗
Modified Source ↗
gdpr compliance and open source ↗
Modified Source ↗
local type inference java cheat sheet ↗
Modified Source ↗
state of opensource security survey ↗
Modified Source ↗
why triaging might be going away ↗
Modified Source ↗
heroku addon beta ↗
Modified Source ↗
npm shrinkwrap reloaded ↗
Modified Source ↗
bower is dead ↗
Modified Source ↗
python mocking 101 ↗
Modified Source ↗
launching state of oss security ↗
Modified Source ↗
announcing net go php ↗
Modified Source ↗
announcing snyk in sonar ↗
Modified Source ↗
77 percent of sites still vulnerable ↗
Modified Source ↗
exposed or not vulnerabilities are dangerous ↗
Modified Source ↗
using the snyk api to find and fix vulnerabilities ↗
Modified Source ↗
to succeed devsecops must die ↗
Modified Source ↗
dont build security tools build developer tools ↗
Modified Source ↗
whats a known vulnerability ↗
Modified Source ↗
where do security patches come from ↗
Modified Source ↗
suppressing issues in snyk ↗
Modified Source ↗
what do open source maintainers know about security ↗
Modified Source ↗
snyk series a ↗
Modified Source ↗
skyscanner gained visibility into their open source vulnerability exposure ↗
Modified Source ↗
case study digital ocean ↗
Modified Source ↗
case study comic relief ↗
Modified Source ↗
attacking an ftp client ↗
Modified Source ↗
introducing groups ↗
Modified Source ↗
snyk named a 2018 gartner cool vendor in application and data security ↗
Modified Source ↗
snyk and lighthouse ↗
Modified Source ↗
tailoring your notifications ↗
Modified Source ↗
zip slip vulnerability ↗
Modified Source ↗
java jvm developer survey launched ↗
Modified Source ↗
behind the disclosure the zip slip vulnerability ↗
Modified Source ↗
javascript and nodejs security the common pitfalls ↗
Modified Source ↗
service accounts ↗
Modified Source ↗
jira integration ↗
Modified Source ↗
over 10 of python packages on pypi are distributed without any license ↗
Modified Source ↗
zip slip vulnerability cheat sheet ↗
Modified Source ↗
container vulnerability management for developers ↗
Modified Source ↗
how to crash an email server with a single email ↗
Modified Source ↗
snyk 22m series b ↗
Modified Source ↗
10 maven security best practices ↗
Modified Source ↗
revisiting unit testing and mocking in python ↗
Modified Source ↗
most common vulnerabilities npm maven ↗
Modified Source ↗
spring boot security best practices ↗
Modified Source ↗
jvm ecosystem report 2018 tools ↗
Modified Source ↗
importing projects via the api ↗
Modified Source ↗
empower developers in security ↗
Modified Source ↗
jvm ecosystem report 2018 platform application ↗
Modified Source ↗
jvm ecosystem report 2018 processes you ↗
Modified Source ↗
launching a free tier version of our container vulnerability management solution ↗
Modified Source ↗
nodejs how even quick async functions can block the event loop starve io ↗
Modified Source ↗
actionable and aggregated slack notifications ↗
Modified Source ↗
a post mortem of the malicious event stream backdoor ↗
Modified Source ↗
intellij plugin ↗
Modified Source ↗
scaling snyk fast with copy paste orgs ↗
Modified Source ↗
codefresh snyk ship fast and securely ↗
Modified Source ↗
jvm ecosystem report 2018 ↗
Modified Source ↗
critical arbitrary code execution vulnerability found in kubernetes ↗
Modified Source ↗
the state of open source security survey ↗
Modified Source ↗
introducing open source security runtime monitoring ↗
Modified Source ↗
serverless security whats left to protect ↗
Modified Source ↗
malicious code found in npm package event stream ↗
Modified Source ↗
faster improved tests for javascript lockfile based projects ↗
Modified Source ↗
2018 year in review ↗
Modified Source ↗
report shows the equifax breach was entirely preventable ↗
Modified Source ↗
snyk highlighted on the thoughtworks technology radar ↗
Modified Source ↗
snyk your next career move ↗
Modified Source ↗
severe security vulnerability in bowers zip archive extraction ↗
Modified Source ↗
my first week at snyk was at our all hands conference ↗
Modified Source ↗
the secret to building a truly successful freemium product and more with guy podjarny ↗
Modified Source ↗
ten npm security best practices ↗
Modified Source ↗
monitoring open source packages at runtime now in open beta ↗
Modified Source ↗
snyks vulnerability database is no longer powering jfrogs xray ↗
Modified Source ↗
launching net support for github bitbucket and gitlab ↗
Modified Source ↗
open source maintainers want to be secure but 70 lack skills ↗
Modified Source ↗
cloud infrastructure drift the good the bad and the ugly ↗
Modified Source ↗
finding open source vulnerabilities within the bitbucket workflow ↗
Modified Source ↗
snyk cli drops support for node js 4 argon ↗
Modified Source ↗
numpy arbitrary code execution vulnerability ↗
Modified Source ↗
so you think your ci cd environment is secure ↗
Modified Source ↗
scanning docker images for key binaries going beyond package managers ↗
Modified Source ↗
a serious security flaw in runc can result in root privilege escalation in docker and kubernetes ↗
Modified Source ↗
78 of vulnerabilities are found in indirect dependencies making remediation complex ↗
Modified Source ↗
security in the container registry ↗
Modified Source ↗
snyking in directory traversal vulnerability exploit in the st package ↗
Modified Source ↗
top ten most popular docker images each contain at least 30 vulnerabilities ↗
Modified Source ↗
introducing the secure developer community ↗
Modified Source ↗
81 believe developers should own security but they arent well equipped ↗
Modified Source ↗
top ten docker images contain over 8000 vulnerable paths ↗
Modified Source ↗
redos vulnerabilities in npm spikes by 143 and xss continues to grow ↗
Modified Source ↗
malicious remote code execution backdoor discovered in the popular bootstrap sass ruby gem ↗
Modified Source ↗
88 increase in application library vulnerabilities over two years ↗
Modified Source ↗
secure your build workflow on bitbucket pipes with snyk ↗
Modified Source ↗
snyking in regular expression denial of service vulnerability exploit in the ms package ↗
Modified Source ↗
cheat sheet 10 bitbucket security best practices ↗
Modified Source ↗
what is package lock json ↗
Modified Source ↗
celebrate international womens day with snyk ↗
Modified Source ↗
introducing experimental integrity policies to node js ↗
Modified Source ↗
security transformation and the three faces of devsecops ↗
Modified Source ↗
snyk joins the continuous delivery foundation as a founding member ↗
Modified Source ↗
190000 users affected by docker hubs security breach now what ↗
Modified Source ↗
the top two most popular docker base images each have over 500 vulnerabilities ↗
Modified Source ↗
snyk provides a critical security layer for communitybridge a new linux foundation platform ↗
Modified Source ↗
80 of developers are not addressing docker security ↗
Modified Source ↗
enriched content on snyks publicly available vulnerability database ↗
Modified Source ↗
take actions to improve security in your docker images ↗
Modified Source ↗
after three years of silence a new jquery prototype pollution vulnerability emerges once again ↗
Modified Source ↗
securing azure repos with snyk ↗
Modified Source ↗
do you know how healthy your net dependencies are ↗
Modified Source ↗
securing bitbucket cloud with snyk ↗
Modified Source ↗
shifting docker security left ↗
Modified Source ↗
protect docker images directly from your container registries ↗
Modified Source ↗
how much do we really know about how packages behave on the npm registry ↗
Modified Source ↗
use personal access tokens with azure repos ↗
Modified Source ↗
add a security md file to your azure repos ↗
Modified Source ↗
scoring security vulnerabilities 101 introducing cvss for cve ↗
Modified Source ↗
rotate azure repos ssh keys and personal access tokens ↗
Modified Source ↗
provide granular permissions and groups for users in azure repos ↗
Modified Source ↗
a denial of service vulnerability discovered in the axios javascript package affecting all versions of the popular http client ↗
Modified Source ↗
understanding amazon s3 security ↗
Modified Source ↗
add security testing to pull requests in azure repos ↗
Modified Source ↗
10 serverless security best practices ↗
Modified Source ↗
remove sensitive data in your files and azure repos history ↗
Modified Source ↗
tightly control access to your azure repos ↗
Modified Source ↗
how to increase serverless observability monitoring and security ↗
Modified Source ↗
jvm ecosystem survey 2019 ↗
Modified Source ↗
dependency health assessing package risk with snyk ↗
Modified Source ↗
never store credentials as code config in azure repos ↗
Modified Source ↗
crlf injection found in popular python dependency ↗
Modified Source ↗
162 security vulnerabilities disclosed in javas top 10 libraries including jackson spring and jetty ↗
Modified Source ↗
how sme lender new10 uses aws and snyk to deliver quickly and securely ↗
Modified Source ↗
whats new in snyk ↗
Modified Source ↗
8 azure repos security best practices ↗
Modified Source ↗
unique to the net ecosystem 75 of the top twenty vulnerabilities have a high severity rating ↗
Modified Source ↗
npm passes the 1 millionth package milestone what can we learn ↗
Modified Source ↗
4 benefits of visualizing your cloud infrastructure ↗
Modified Source ↗
snyk voted next european unicorn for b2b enterprise ↗
Modified Source ↗
new oreilly book securing open source libraries by guy podjarny ↗
Modified Source ↗
yet another malicious package found in npm targeting cryptocurrency wallets ↗
Modified Source ↗
serverless is great but what about the security of my aws lambda functions and their dependencies ↗
Modified Source ↗
best practices for secrets management in serverless applications ↗
Modified Source ↗
pci standards open source security requirements how to comply ↗
Modified Source ↗
snyk research team discovers severe prototype pollution security vulnerabilities affecting all versions of lodash ↗
Modified Source ↗
ruby gem strong password found to contain remote code execution code in a malicious version further strengthening worries of growth in supply chain attacks ↗
Modified Source ↗
best practices for rolling out snyk ↗
Modified Source ↗
fix open source vulnerabilities directly from your eclipse ide ↗
Modified Source ↗
snyk has acquired devseccon ↗
Modified Source ↗
remote code execution cross site scripting and denial of service vulnerabilities account for 2 3 of known vulnerabilities in net ecosystem ↗
Modified Source ↗
scaling developer first security ↗
Modified Source ↗
10 eclipse plugins you shouldnt code without ↗
Modified Source ↗
a technical analysis of the capital one cloud misconfiguration breach ↗
Modified Source ↗
net open source security insights ↗
Modified Source ↗
everything you wanted to know about addressing security vulnerabilities in linux based containers ↗
Modified Source ↗
securing go modules made easy ↗
Modified Source ↗
announcing new container registries integrations ↗
Modified Source ↗
staying ahead of security vulnerabilities with security patches ↗
Modified Source ↗
10 java security best practices ↗
Modified Source ↗
kubernetes open sourced their security audit what can we learn ↗
Modified Source ↗
open source security with oreilly author guy podjarny ↗
Modified Source ↗
securing artifactory using snyk ↗
Modified Source ↗
automating open source security scanning with snyk and circleci ↗
Modified Source ↗
a year old dormant malicious remote code execution vulnerability discovered in webmin ↗
Modified Source ↗
jackson deserialization vulnerability ↗
Modified Source ↗
6 stages of refactoring a jest test case ↗
Modified Source ↗
mastering node js version management and npm registry sources like a pro ↗
Modified Source ↗
sequelize orm npm library found vulnerable to sql injection attacks ↗
Modified Source ↗
code execution back door found in rubys rest client library ↗
Modified Source ↗
the secure developer talking devsecops in azure with microsofts victoria almazova ↗
Modified Source ↗
2019 side by side comparison of angular and react security vulnerabilities ↗
Modified Source ↗
snyk raises 70m to accelerate dev first security ↗
Modified Source ↗
shifting licensing left helping legal and developers cooperate around licensing issues ↗
Modified Source ↗
secure your kubernetes applications with snyk container ↗
Modified Source ↗
why npm lockfiles can be a security blindspot for injecting malicious modules ↗
Modified Source ↗
making climate positive changes ↗
Modified Source ↗
trend micro and snyk partner to deliver complete remediation to secure containers ↗
Modified Source ↗
snyk joins cloudbees new technical alliance partner program as premier launch member ↗
Modified Source ↗
angular vs react security bakeoff 2019 ↗
Modified Source ↗
using open policy agent opa for cloud security and compliance ↗
Modified Source ↗
a snyk peek into node js and npms state of open source security report 2019 ↗
Modified Source ↗
angular vs react the security risk of indirect dependencies ↗
Modified Source ↗
container security throughout the sdlc ↗
Modified Source ↗
shifting security left means culture not just tools ↗
Modified Source ↗
a recap from our latest pci webinar and compliance tips from deliveroo ↗
Modified Source ↗
putting container security in the hands of developers ↗
Modified Source ↗
whats so wild about exploits in the wild and how can we prioritize accordingly ↗
Modified Source ↗
shipping kubernetes native applications with confidence ↗
Modified Source ↗
comparing react and angular secure coding practices ↗
Modified Source ↗
using third party content securely ↗
Modified Source ↗
javascript frameworks security report 2019 ↗
Modified Source ↗
84 percent of all websites impacted by jquery xss vulnerabilities ↗
Modified Source ↗
scaling security through devsecops ↗
Modified Source ↗
creating a language for security with chefs adam jacob ↗
Modified Source ↗
keep your dependencies up to date enable auto upgrades with snyk ↗
Modified Source ↗
from image security to workload security ↗
Modified Source ↗
see snyk and github in action at github universe ↗
Modified Source ↗
uncharted territory discovering vulnerabilities in public helm charts ↗
Modified Source ↗
security digital transformation with james kaplan ↗
Modified Source ↗
showing application vulnerabilities in kubernetes native tooling ↗
Modified Source ↗
deploying a gatsby site to github pages from travis ci ↗
Modified Source ↗
open source vulnerabilities and security with microsofts jeff mcaffer ↗
Modified Source ↗
snyks defining values ↗
Modified Source ↗
understanding filesystem takeover vulnerabilities in npm javascript package manager ↗
Modified Source ↗
snyk unifies open source and container security for coveo ↗
Modified Source ↗
integrating actionable security in your ci cd workflow and build systems with snyk tests ↗
Modified Source ↗
48 percent see security a major constraint on the ability to deliver software quickly ↗
Modified Source ↗
snyk receives best ceo award ↗
Modified Source ↗
snyk closes 150m ↗
Modified Source ↗
is localstorage safe to use ↗
Modified Source ↗
malicious packages found to be typo squatting in pypi ↗
Modified Source ↗
devsecops insights 2020 ↗
Modified Source ↗
navigating your own career growth in a hyper growth startup ↗
Modified Source ↗
intellij idea dominates the ide market with 62 adoption among jvm developers ↗
Modified Source ↗
january in review funding news devsecops insights study and much more ↗
Modified Source ↗
building security into your azure devops pipeline ↗
Modified Source ↗
29 percent of highest security integration orgs endure friction when collaborating ↗
Modified Source ↗
the cost of a security breach ↗
Modified Source ↗
protecting our culture as we hyperscale ↗
Modified Source ↗
31 percent dont track application dependencies and 38 only track direct dependencies ↗
Modified Source ↗
kotlin overtakes scala and clojure to become the 2nd most popular language on the jvm ↗
Modified Source ↗
36 of developers switched from oracle jdk to an alternate openjdk distribution over the last year ↗
Modified Source ↗
streamline kubernetes security in amazon web services ↗
Modified Source ↗
building a culture of digital trust ↗
Modified Source ↗
spring dominates the java ecosystem with 60 using it for their main applications ↗
Modified Source ↗
86 percent of security and tech roles agree that security is a shared responsibility ↗
Modified Source ↗
find and fix vulnerabilities in artifactory container repositories ↗
Modified Source ↗
developers dont want to leave java 8 as 64 hold firm on their preferred release ↗
Modified Source ↗
jvm ecosystem report 2020 ↗
Modified Source ↗
security breach leaks the personal data of all 6 5 million israeli voters ↗
Modified Source ↗
node js release fixes a critical http security vulnerability ↗
Modified Source ↗
snyk rapid7 partnership ↗
Modified Source ↗
how can a content security policy prevent xss and other vulnerabilities ↗
Modified Source ↗
5 ways snyk helps you to prioritize and fix your vulnerabilities ↗
Modified Source ↗
automating kubernetes workload security reporting ↗
Modified Source ↗
snyk named to crns security 100 list ↗
Modified Source ↗
ghostcat breach affects all tomcat versions ↗
Modified Source ↗
snyk partners with greenkeeper to help developers proactively maintain dependency health ↗
Modified Source ↗
february in review jvm ecosystem report python and container updates and more ↗
Modified Source ↗
rsa 2020 who we met and what we learned ↗
Modified Source ↗
cloud transforms it security appsec ↗
Modified Source ↗
is your website vulnerable lets fix it ↗
Modified Source ↗
angularjs security ↗
Modified Source ↗
fastify nodejs improves json security ↗
Modified Source ↗
popular python library urllib3 subject to a denial of service vulnerability ↗
Modified Source ↗
how to detect and fix kubernetes access restriction vulnerability cve 2019 11249 ↗
Modified Source ↗
a call to growing tech companies how to move the needle on gender equality together ↗
Modified Source ↗
coronavirus adapting fully remote ↗
Modified Source ↗
12 things for successful devsecops ↗
Modified Source ↗
to our community from the snyk team ↗
Modified Source ↗
opensourcesecurity 2020survey ↗
Modified Source ↗
creating an automated cloud infrastructure testing tool with terraform and ↗
Modified Source ↗
what is a backdoor ↗
Modified Source ↗
django security tips ↗
Modified Source ↗
ubi to minimize container vulnerabilities ↗
Modified Source ↗
march in review security news ↗
Modified Source ↗
prototype pollution minimist ↗
Modified Source ↗
working from home tips ↗
Modified Source ↗
shift left enhanced security pull requests ↗
Modified Source ↗
secure code review ↗
Modified Source ↗
yarn 2 intro ↗
Modified Source ↗
snyk atlassian remote summit ↗
Modified Source ↗
vuln cost security scanner vs code ↗
Modified Source ↗
vulnerable gradle plugin ↗
Modified Source ↗
yarn 2 plugins ↗
Modified Source ↗
vs code extension building auto cicd with github actions ↗
Modified Source ↗
snyk aws partnership vuln scanning ↗
Modified Source ↗
vulnerability disclosure program ↗
Modified Source ↗
dependency management tools python ↗
Modified Source ↗
responsible disclosure ↗
Modified Source ↗
fix insecure kubernetes configuration ↗
Modified Source ↗
recap kubernetes configuration security ↗
Modified Source ↗
developer first license compliance ↗
Modified Source ↗
snyk container certified vmware pks partner ready ↗
Modified Source ↗
license compliance management ↗
Modified Source ↗
snyk amazon linux 2 ready designation ↗
Modified Source ↗
finding meaning amidst unknown ↗
Modified Source ↗
why did is promise happen and what can we learn from it ↗
Modified Source ↗
mental health awareness month ↗
Modified Source ↗
snyk red hat empower openshift developers ↗
Modified Source ↗
snyk aws lambda ready designation ↗
Modified Source ↗
open source software security ↗
Modified Source ↗
manage risk with snyk project tags ↗
Modified Source ↗
website security score explained ↗
Modified Source ↗
snyk launches devsecops hub ↗
Modified Source ↗
why snyk wins open source security battle ↗
Modified Source ↗
three mental health awareness lessons for managers ↗
Modified Source ↗
java turns 25 ↗
Modified Source ↗
managing license compliance ↗
Modified Source ↗
open source tools terraform code testing ↗
Modified Source ↗
3 big amazon s3 vulnerabilities you may be missing ↗
Modified Source ↗
manage drift from manual changes terraform ↗
Modified Source ↗
engineering equal opportunities at snyk ↗
Modified Source ↗
manage multiple terraform versions ↗
Modified Source ↗
detecting vulnerabilities in container images ↗
Modified Source ↗
mitigating clickjacking the devsecops way ↗
Modified Source ↗
how to manage terraform state ↗
Modified Source ↗
celebrating pride month snyk style ↗
Modified Source ↗
snyk support for azure repos server ↗
Modified Source ↗
sum list of numbers in java ↗
Modified Source ↗
fix vulnerabilities with ml powered merge advice ↗
Modified Source ↗
sdr during covid 19 snyk style ↗
Modified Source ↗
demystifying http request smuggling ↗
Modified Source ↗
git the easy way using rebase part i ↗
Modified Source ↗
checking helm charts for security misconfigurations ↗
Modified Source ↗
our privilege is our responsibility ↗
Modified Source ↗
git the easy way using rebase part ii ↗
Modified Source ↗
enhanced security for bitbucket cloud development ↗
Modified Source ↗
discover package vulnerabilities with snyk jsdelivr integration ↗
Modified Source ↗
aws circleci snyk webinar devsecops journey ↗
Modified Source ↗
manage multiple terraform environments ↗
Modified Source ↗
how to maintain npm dependencies in your project ↗
Modified Source ↗
snyks developer first prioritization capabilities ↗
Modified Source ↗
lgbtq in tech part ii ↗
Modified Source ↗
the devops virtual conference does ↗
Modified Source ↗
lgbtq in tech part i ↗
Modified Source ↗
regular expression denial of service in websocket extensions ↗
Modified Source ↗
navigate 3 trends in financial services with devsecops ↗
Modified Source ↗
sour mint malicious sdk ↗
Modified Source ↗
secure amazon elastic kubernetes service workloads ↗
Modified Source ↗
instant security information with the snyk security badge ↗
Modified Source ↗
import existing infrastructure into terraform ↗
Modified Source ↗
top tips for handling remote working fatigue ↗
Modified Source ↗
helping developers prioritize security backlog ↗
Modified Source ↗
optimizing prioritization with deep application level context ↗
Modified Source ↗
strength through diversity ↗
Modified Source ↗
angular security best practices ↗
Modified Source ↗
arbitrary file write via archive extraction in go rpmutils ↗
Modified Source ↗
message brokers ↗
Modified Source ↗
snyk named to crn 2020 emerging vendor list ↗
Modified Source ↗
snyk collects best place to work awards ↗
Modified Source ↗
snyk priority score ↗
Modified Source ↗
reachable vulnerabilities ↗
Modified Source ↗
java dependency management ↗
Modified Source ↗
gartner guide highlights importance of software composition analysis ↗
Modified Source ↗
application security trends esg research ↗
Modified Source ↗
sourmint malicious code ad fraud and data leak in ios ↗
Modified Source ↗
prioritizing vulnerabilities in kubernetes deployments ↗
Modified Source ↗
fixing vulnerabilities in maven projects ↗
Modified Source ↗
5 tips for using the rego language for open policy agent opa ↗
Modified Source ↗
infrastructure as code security ↗
Modified Source ↗
career growth in a scale up world ↗
Modified Source ↗
building a secure amazon s3 bucket aws ↗
Modified Source ↗
arbitrary code execution in js grunt ↗
Modified Source ↗
prototype pollution in express fileupload ↗
Modified Source ↗
enhancing security testing for go projects ↗
Modified Source ↗
snyk trend solution for solving open source development risks ↗
Modified Source ↗
snyk integration with red hat codeready dependency analytics ↗
Modified Source ↗
prioritizing container vulnerabilities with exploit maturity ↗
Modified Source ↗
scaling security with devsecops forbes cloud 100 company ↗
Modified Source ↗
web application vulnerabilities prioritisation ↗
Modified Source ↗
snyk closes 200m to modernize security industry ↗
Modified Source ↗
shift security left with a new pycharm plugin ↗
Modified Source ↗
snyk integration with aws ecr and lambda ↗
Modified Source ↗
snyk and rapid7 enhance security for cloud native applications ↗
Modified Source ↗
enabling application security management at scale ↗
Modified Source ↗
snyk trek10 aws secure serverless cicd deployments ↗
Modified Source ↗
what is bsd license ↗
Modified Source ↗
a glimpse into diversity at snyk ↗
Modified Source ↗
sourmint malicious sdk research write up ↗
Modified Source ↗
how to scale successfully with snyk ↗
Modified Source ↗
owasp top 10 vulnerabilities ↗
Modified Source ↗
how to deploy a vue js jamstack application on netlify ↗
Modified Source ↗
accelerating developer first vision with deepcode ↗
Modified Source ↗
snyk security information in github code scanning ↗
Modified Source ↗
jhipster security scanning ↗
Modified Source ↗
snykcon day two wrap up ↗
Modified Source ↗
snyk and secure code warrior ↗
Modified Source ↗
why your team should attend snykcon 2020 ↗
Modified Source ↗
developer first sast with snyk code ↗
Modified Source ↗
vulnerability remediation process ↗
Modified Source ↗
remote code execution rce sourmint ↗
Modified Source ↗
gradle plugin by snyk gradle dependencies scanning ↗
Modified Source ↗
scanning arm container images with snyk ↗
Modified Source ↗
github actions to securely publish npm packages ↗
Modified Source ↗
lessons from the node js security working group ↗
Modified Source ↗
snykcon day one wrap up ↗
Modified Source ↗
regular expression denial of service redos in uaparser js ↗
Modified Source ↗
enterprise security at scale ↗
Modified Source ↗
tips to scale your devsecops organization ↗
Modified Source ↗
happiness in the year of covid 19 ↗
Modified Source ↗
how atlassian ciso built a world class product security team ↗
Modified Source ↗
rpm package manager rpm package security scanning with snyk ↗
Modified Source ↗
security risk management ↗
Modified Source ↗
how we promote inclusivity in our job descriptions ↗
Modified Source ↗
privileged docker containers ↗
Modified Source ↗
kubernetes operators automating the release process ↗
Modified Source ↗
the new improved snyk container cli ↗
Modified Source ↗
container image formats ↗
Modified Source ↗
java logging what should you log and what not ↗
Modified Source ↗
international mens day its time to talk ↗
Modified Source ↗
python poetry package manager ↗
Modified Source ↗
test your github projects for known vulnerabilities ↗
Modified Source ↗
snyk cli cheat sheet ↗
Modified Source ↗
snyk cli cheat sheet ↗
Modified Source ↗
snyk cli cheat sheet ↗
Modified Source ↗
snyk and docker security guide for developers ↗
Modified Source ↗
detect vulnerabilities in dockerfiles directly from git ↗
Modified Source ↗
launching the snyk community outreach internship program ↗
Modified Source ↗
docker for java developers ↗
Modified Source ↗
devsecops tools for open source projects in javascript and node js ↗
Modified Source ↗
10 git aliases for faster and productive git workflow ↗
Modified Source ↗
serialization and deserialization in java ↗
Modified Source ↗
command injection ↗
Modified Source ↗
infrastructure as code tools ↗
Modified Source ↗
buffer overflow in chromium affecting multiple packages ↗
Modified Source ↗
command line tools for containers ↗
Modified Source ↗
cheatsheet top 10 application security acronyms ↗
Modified Source ↗
kernel privilege escalation ↗
Modified Source ↗
an alternative way to lead engineering teams ↗
Modified Source ↗
blazing the trail for cloud native application security ↗
Modified Source ↗
announcing go security with snyk ↗
Modified Source ↗
detect externalip kubernetes vulnerability with snyk ↗
Modified Source ↗
container linux security and relative importance ↗
Modified Source ↗
10 tips for getting that conference cfp accepted ↗
Modified Source ↗
security testing git based gradle projects lockfile ↗
Modified Source ↗
securing kubernetes application development with snyk and tilt ↗
Modified Source ↗
what makes fastify a successful project ↗
Modified Source ↗
golang security access restriction bypass vulnerability jwt ↗
Modified Source ↗
2020 q2 in review state of open source security report devsecops hub ↗
Modified Source ↗
git checkout remote branch ↗
Modified Source ↗
third party javascript concerns ↗
Modified Source ↗
aws vulnerability scanning using the snyk integration ↗
Modified Source ↗
2020 q3 in review snyk deepcode angular security best practices ↗
Modified Source ↗
2020 q1 in review jvm ecosystem report devsecops insights ↗
Modified Source ↗
typosquatting attacks ↗
Modified Source ↗
goodbye 2020 lookout 2021 ↗
Modified Source ↗
2020 q4 in review ios remote code execution developer first sast ↗
Modified Source ↗
cache poisoning in popular open source packages ↗
Modified Source ↗
applying risk management to devops practices ↗
Modified Source ↗
identify security vulnerabilities with reachable vulnerabilities for github ↗
Modified Source ↗
prioritize fixes with reachable vulnerabilities for github ↗
Modified Source ↗
docker for node js developers 5 things you need to know ↗
Modified Source ↗
snyk rapid7 to provide holistic risk assessment solution ↗
Modified Source ↗
kubernetes securitycontext linux capabilities ↗
Modified Source ↗
security vulnerability exploits threats ↗
Modified Source ↗
go security cheatsheet for go developers ↗
Modified Source ↗
learnings from our 2021 kickoff ↗
Modified Source ↗
the state of cloud native application security survey 2021 ↗
Modified Source ↗
extensibility and the snyk api ↗
Modified Source ↗
dockerfile optimization and docker image security scanning ↗
Modified Source ↗
java configuration prevent security misconfigurations ↗
Modified Source ↗
snyk kicks off community outreach internship program ↗
Modified Source ↗
snyk iac scanning enhancements include aws infrastructure as code ↗
Modified Source ↗
our journey to today ↗
Modified Source ↗
solarwinds orion security breach a shift in the software supply chain paradigm ↗
Modified Source ↗
snyk expands into asia pacific japan ↗
Modified Source ↗
10 kubernetes security context settings you should understand ↗
Modified Source ↗
java ecosystem survey 2021 ↗
Modified Source ↗
hacking docker containers by exploiting base image vulnerabilities ↗
Modified Source ↗
devops security ↗
Modified Source ↗
security incident management snyk opsgenie integration ↗
Modified Source ↗
snyks new vulnerability cards fix issues fast with a new look and feel ↗
Modified Source ↗
java yaml parser with snakeyaml ↗
Modified Source ↗
devops tools ↗
Modified Source ↗
java code analysis solving java security issues in spring mvc app ↗
Modified Source ↗
defining developer first container security ↗
Modified Source ↗
quay vulnerability scanning with snyk ↗
Modified Source ↗
sql injection cheat sheet ↗
Modified Source ↗
application security automation github ↗
Modified Source ↗
5 ways to prevent code injection in javascript and node js ↗
Modified Source ↗
5 ways to prevent code injection in javascript and node js ↗
Modified Source ↗
5 ways to prevent code injection in javascript and node js ↗
Modified Source ↗
5 ways to prevent code injection in javascript and node js ↗
Modified Source ↗
issuing fix prs to update dockerfiles ↗
Modified Source ↗
backstage integration with the snyk api ↗
Modified Source ↗
scanning harbor registry images for vulnerabilities snyk ↗
Modified Source ↗
python language support now beta in snyk code ↗
Modified Source ↗
secure coding with jetbrains ide plugin ↗
Modified Source ↗
secure coding snyk code ignore feature twist ↗
Modified Source ↗
secure elixir development with snyk ↗
Modified Source ↗
view and report snyk infrastructure as code iac configuration issues ↗
Modified Source ↗
how to fix java security issues while coding in intellij idea ↗
Modified Source ↗
snyk at snyk enabling kubernetes rbac for snyks developers ↗
Modified Source ↗
snyk maven plugin integrated security vulnerability scanning for developers ↗
Modified Source ↗
secure development for teams snyk team product tier ↗
Modified Source ↗
intuit roundtable breaking silos engaging security developer communities ↗
Modified Source ↗
sast tools ↗
Modified Source ↗
prevent cloud misconfigurations hashicorp terraform snyk iac ↗
Modified Source ↗
suitecrm phar deserialization vulnerability to code execution ↗
Modified Source ↗
snyk iac public beta introduces terraform plan analysis ↗
Modified Source ↗
github security code scanning ↗
Modified Source ↗
code dx 5 3 integrates with snyk for comprehensive vulnerability management ↗
Modified Source ↗
6 reasons to use source code analysis ↗
Modified Source ↗
celebrating four years of developer first integrations at atlassian team 21 ↗
Modified Source ↗
snyk code now available free sast ↗
Modified Source ↗
performance in opa rego bottom up and top down ↗
Modified Source ↗
appsec 2021 reddit ↗
Modified Source ↗
testing php composer security vulnerabilities snyk ↗
Modified Source ↗
npm security malicious code in oss npm packages ↗
Modified Source ↗
fossid joins snyk extends dev first c security ↗
Modified Source ↗
trend micro launches cloud one open source security powered by snyk ↗
Modified Source ↗
snyker spotlight jeff yoshimura asian american heritage aapi month ↗
Modified Source ↗
misconfigurations known unpatched vulnerabilities cloud native application security ↗
Modified Source ↗
snyk aws marketplace private offer sppo ↗
Modified Source ↗
vulnerable visual studio code extensions marketplace ↗
Modified Source ↗
snyk visionary 2021 gartner magic quadrant for ast ↗
Modified Source ↗
continuous dependency updates improving processes front loading pain ↗
Modified Source ↗
snyk takes on node js ecosystem vulnerability disclosure program ↗
Modified Source ↗
understanding software supply chain security requirements cybersecurity executive order ↗
Modified Source ↗
understanding software supply chain security requirements cybersecurity executive order ↗
Modified Source ↗
understanding software supply chain security requirements cybersecurity executive order ↗
Modified Source ↗
understanding software supply chain security requirements cybersecurity executive order ↗
Modified Source ↗
understanding software supply chain security requirements cybersecurity executive order ↗
Modified Source ↗
early access to snyk features snyk preview ↗
Modified Source ↗
secure development visual studio snyk open source ↗
Modified Source ↗
announcing snykcon 2021 build securely ↗
Modified Source ↗
python now fully supported in snyk code ↗
Modified Source ↗
snyk debuts on 2021 cnbc disruptor 50 list at 15 ↗
Modified Source ↗
devseccon24 2021 24 hours of development security and inclusivity ↗
Modified Source ↗
automate vulnerability scanning in aws codepipeline with snyk ↗
Modified Source ↗
give employees the flexibility to do their best work ↗
Modified Source ↗
advancing sbom standards snyk spdx ↗
Modified Source ↗
snyker spotlight reflecting on juneteenth ↗
Modified Source ↗
easily map snyk vulnerabilities to cortex services ↗
Modified Source ↗
snyk native integration atlassian bitbucket cloud security ↗
Modified Source ↗
snyker spotlight proud of the home i found at snyk ↗
Modified Source ↗
scan aws cloudformation misconfigurations snyk iac ↗
Modified Source ↗
cant compare sast tools lists test suites benchmarks ↗
Modified Source ↗
snykcon 2021 5 reasons to submit your talk ↗
Modified Source ↗
risks of open source software ↗
Modified Source ↗
snyk container extension aws cloudformation registry ↗
Modified Source ↗
oreilly book cloud native application security developer first security ↗
Modified Source ↗
snykcon 2021 excitement starting cfp ending ↗
Modified Source ↗
snyk for secure java development ↗
Modified Source ↗
cloud application security ↗
Modified Source ↗
prevent php code injection ↗
Modified Source ↗
visibility scalability relationships secure development phil guimond viacomcbs ↗
Modified Source ↗
snyker spotlight what ive learned from my career change ↗
Modified Source ↗
managing node js docker images in github packages using github actions ↗
Modified Source ↗
hardening aws eks security rbac secure imds audit logging ↗
Modified Source ↗
snyk at rsac 2021 ml in sast distraction or disruption ↗
Modified Source ↗
tips best practices building secure container images ↗
Modified Source ↗
looking back pride month 2021 snyk ↗
Modified Source ↗
tips for hardening container image security strategy ↗
Modified Source ↗
why you should upgrade to maven version 3 8 1 ↗
Modified Source ↗
sast tools speed comparison snyk code sonarqube lgtm ↗
Modified Source ↗
hardening amazon eks security ↗
Modified Source ↗
snyk security policies ↗
Modified Source ↗
snyk code security scanning c sharp dot net ↗
Modified Source ↗
how we normalize authentication at snyk with gloo edge ↗
Modified Source ↗
getting started snyk for secure python development ↗
Modified Source ↗
social media for security intelligence ↗
Modified Source ↗